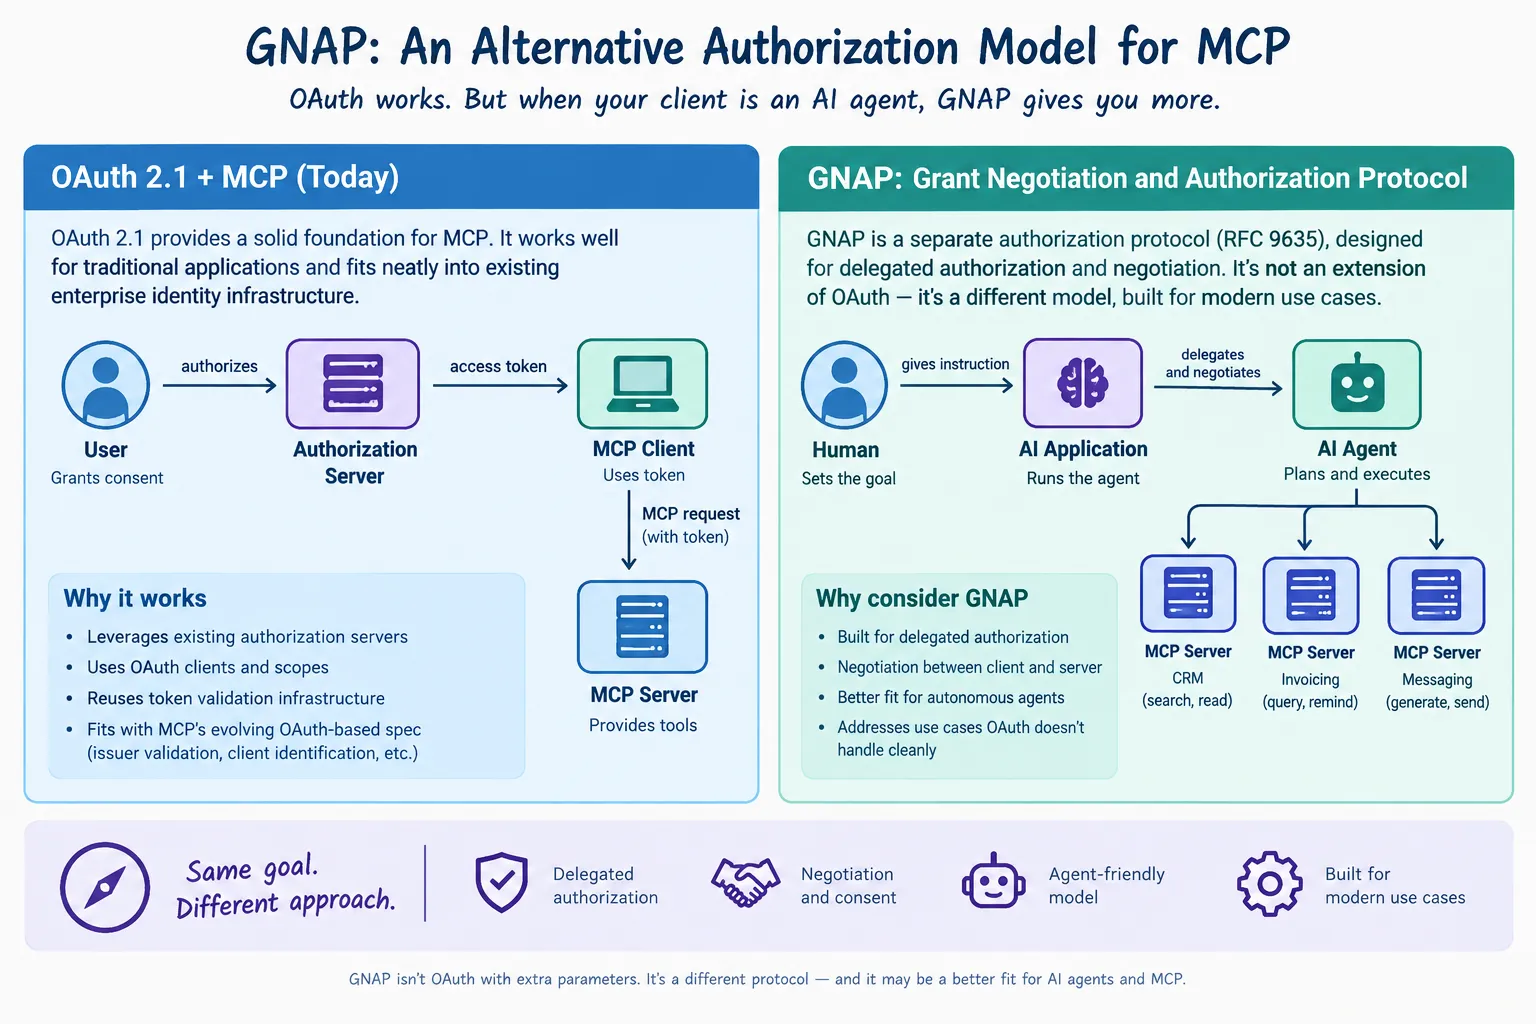
GNAP: An Alternative Authorization Model for MCP
OAuth2 has been around long enough that it is easy to forget just how much machinery has accumulated around it.
Read article: GNAP: An Alternative Authorization Model for MCP49 articles tagged OAuth2.
OAuth2 has been around long enough that it is easy to forget just how much machinery has accumulated around it.
Read article: GNAP: An Alternative Authorization Model for MCPNote, We are exclusively talking about SAML2 in this story.
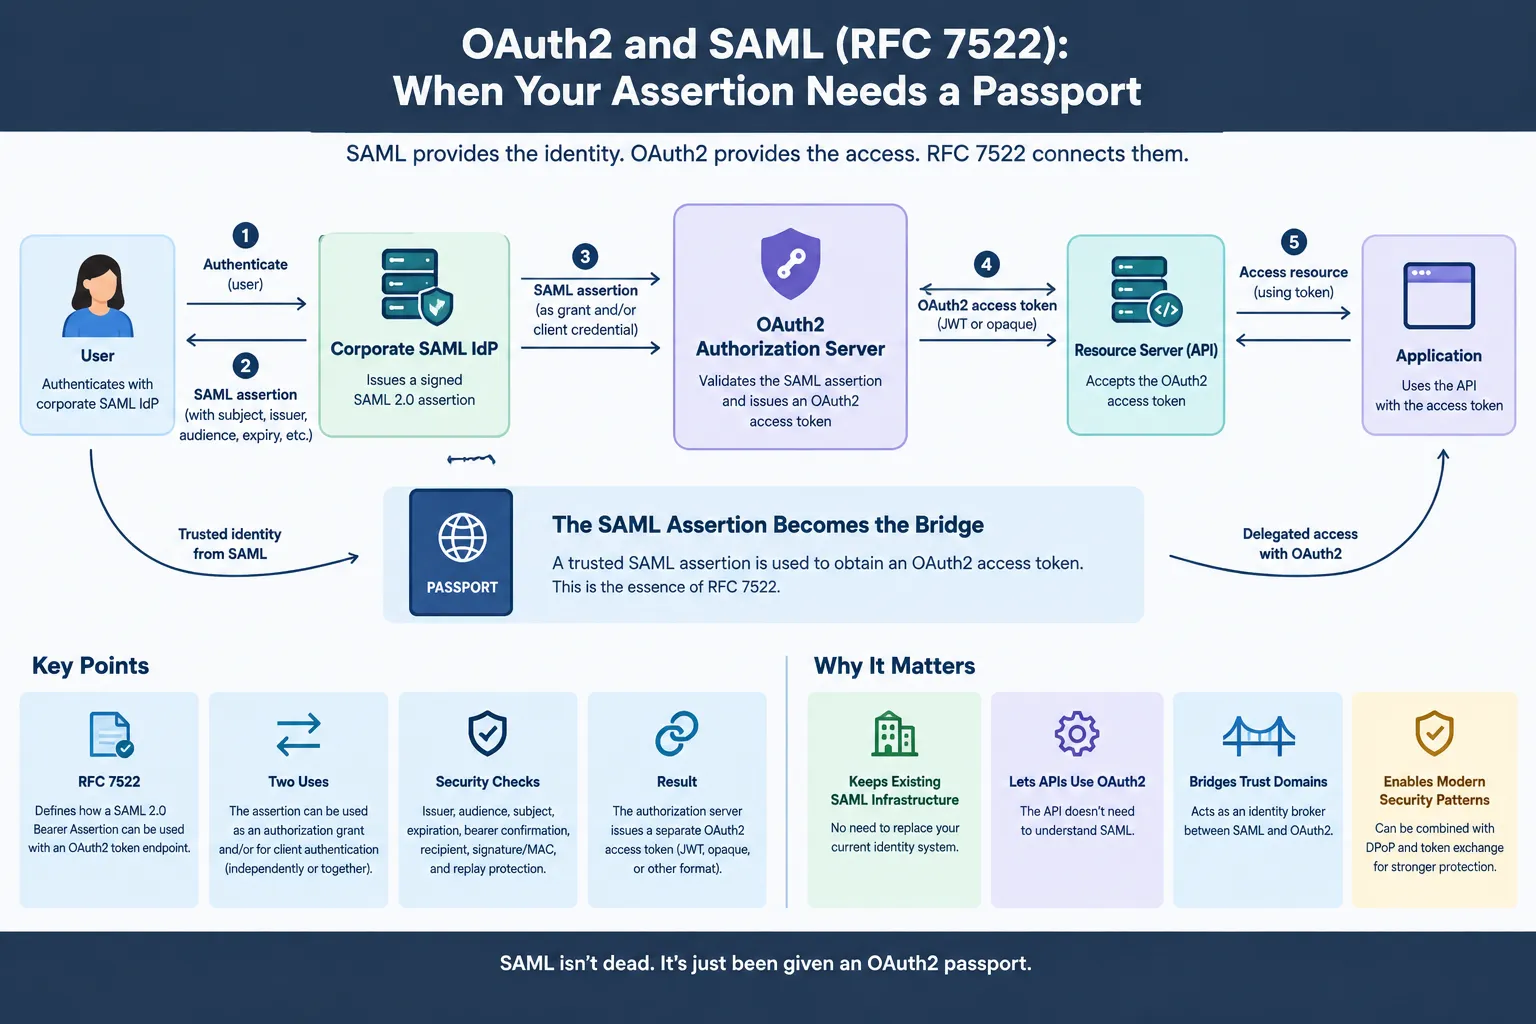
Read article: OAuth2 and SAML(RFC 7522): When Your Assertion Needs a PassportOAuth2 has a fairly straightforward model. A client authenticates to an authorization server, obtains an access token, and uses that token to access a protected resource.
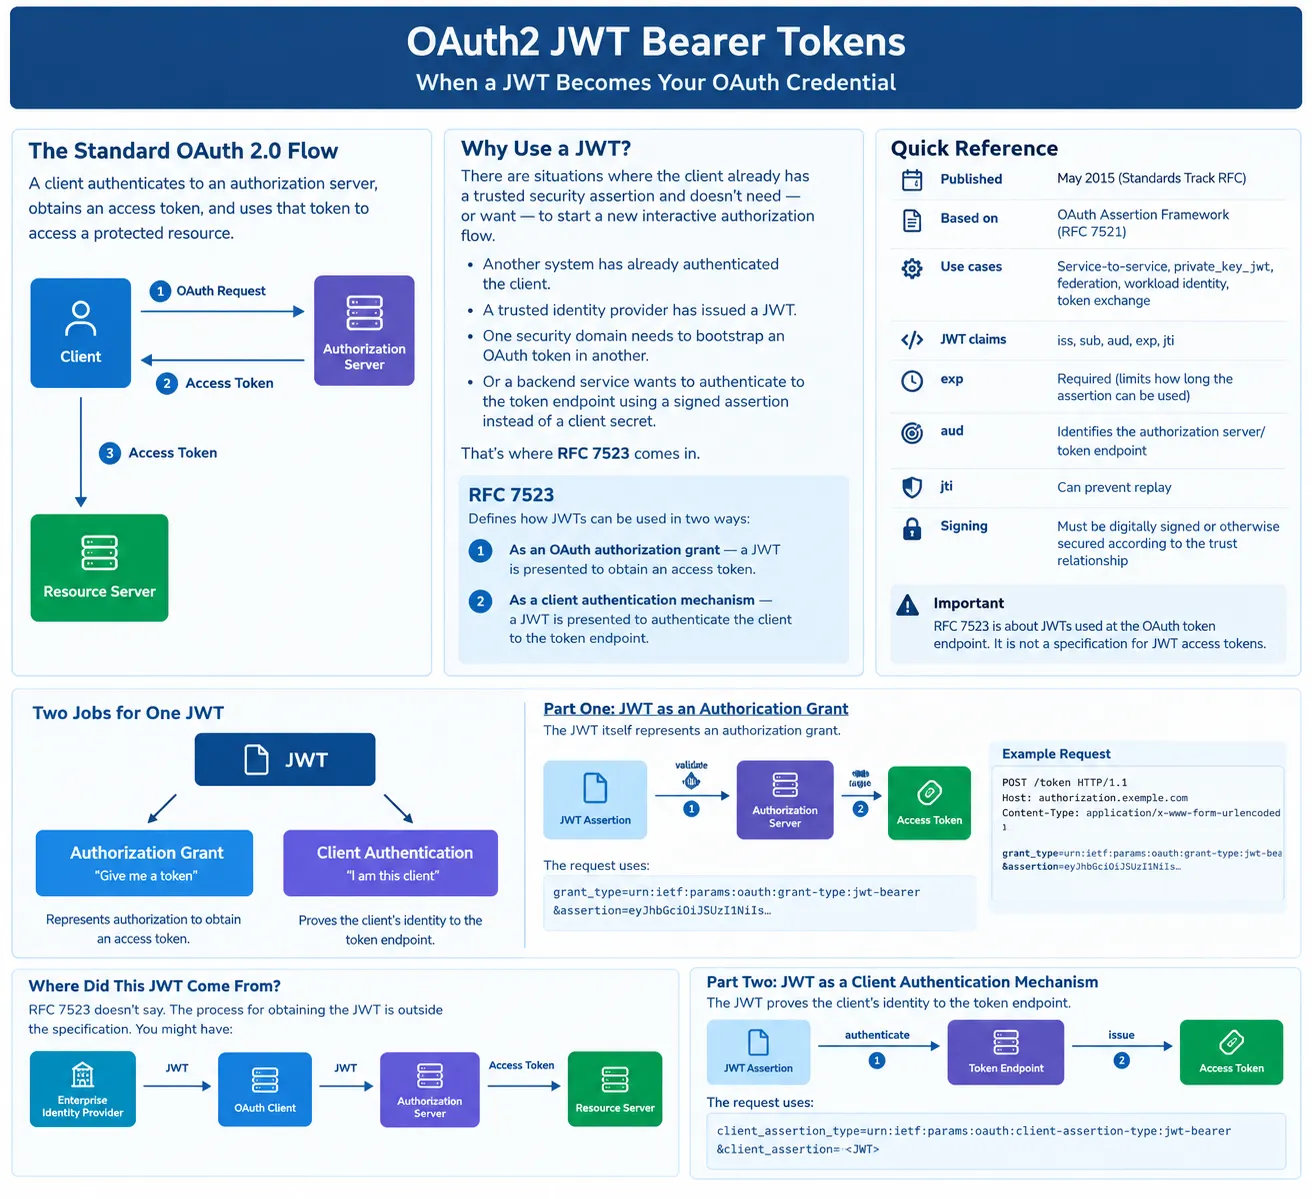
Read article: OAuth2 JWT Bearer Tokens (RFC-7523): When a JWT Becomes Your OAuth2 CredentialThe original three-legged OAuth2 use case has been a well-understood use case for a long-time.
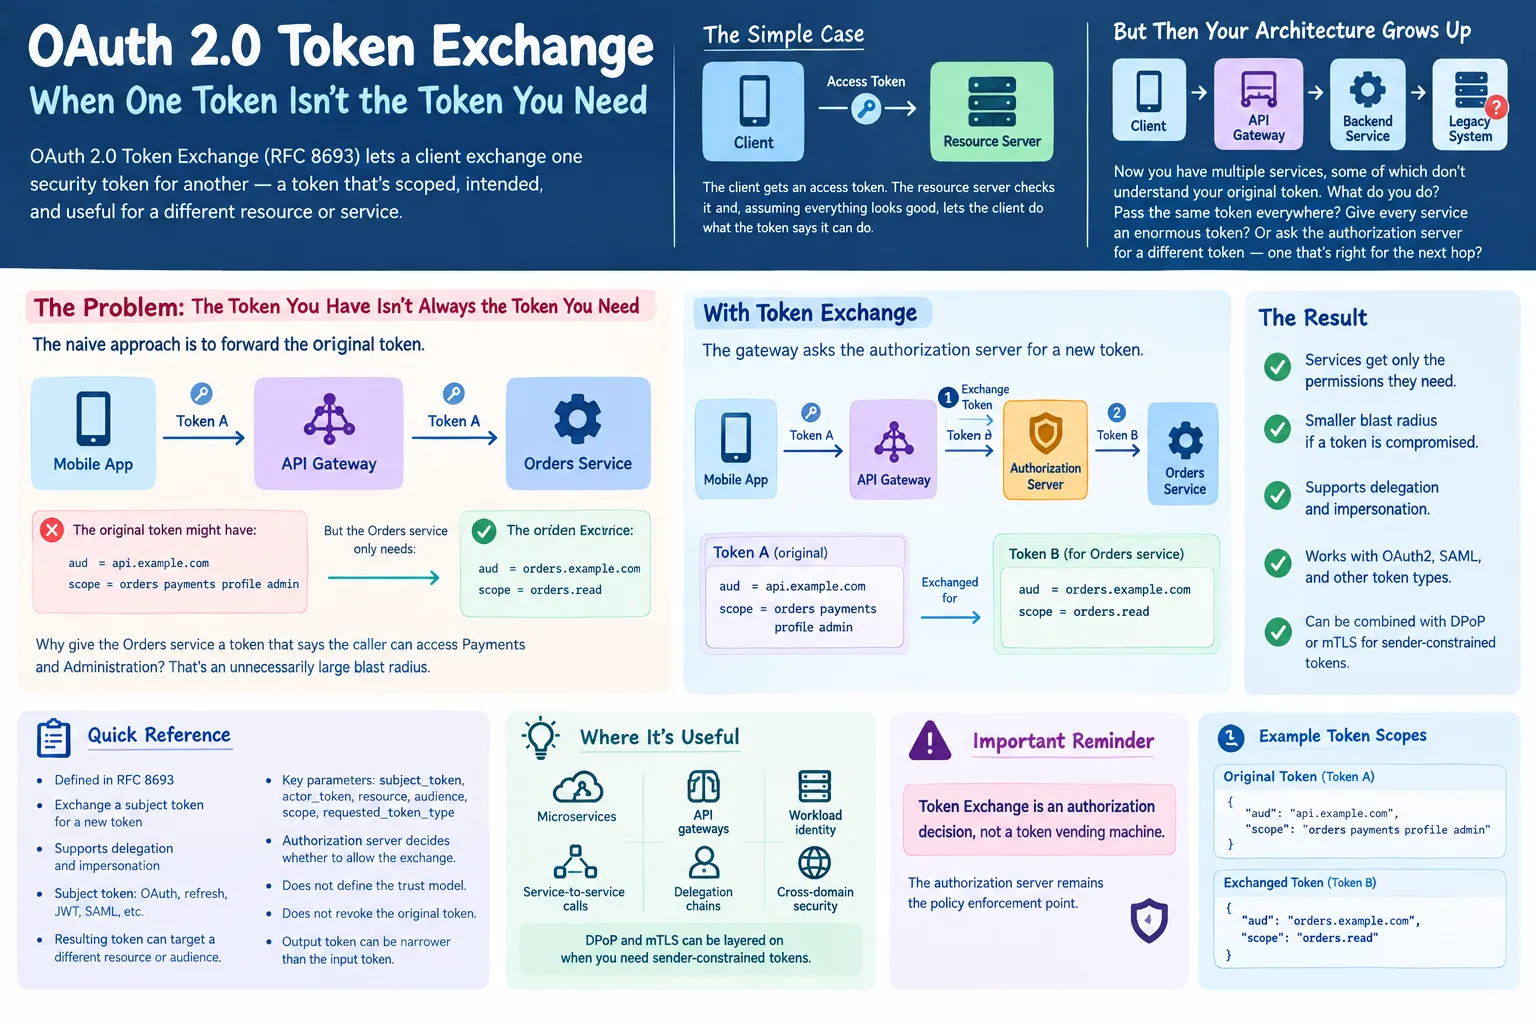
Read article: OAuth 2.0 Token Exchange: When One Token Isn’t the Token You NeedOAuth2 was designed around the assumption that the client can open a browser.
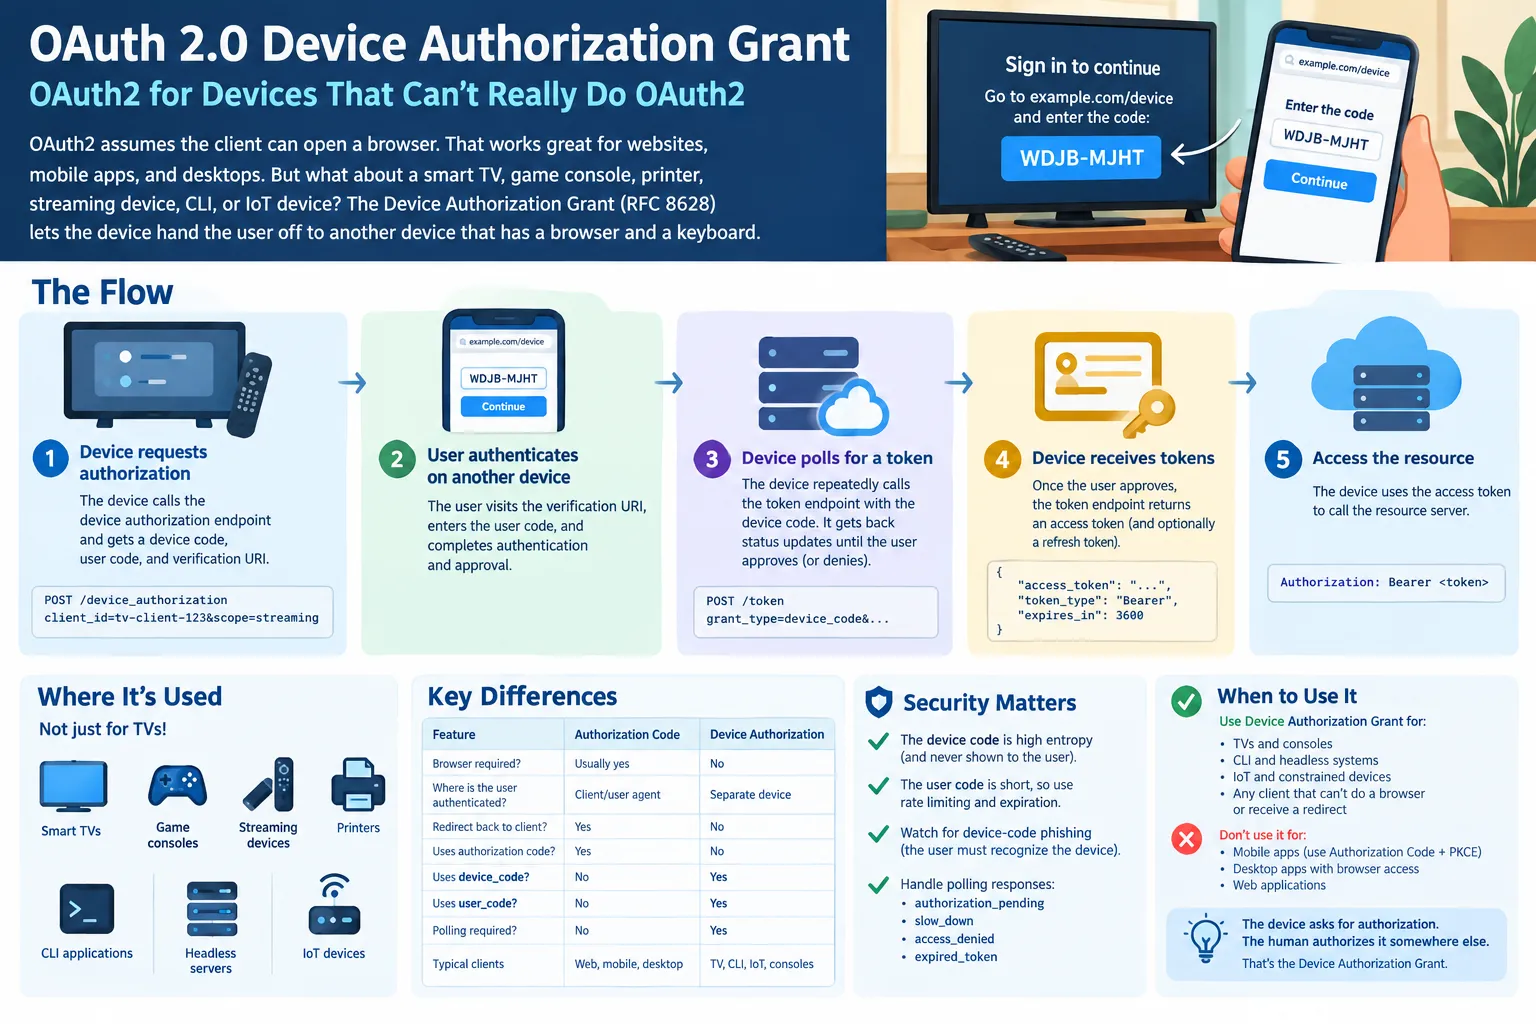
Read article: OAuth2 Device Authorization Grant: OAuth2 for Devices That Can’t Really Do OAuth2Disclaimer: This article was written in Q3,2026. It is current as of that date. The OAuth 2.1 draft proposals have not yet been published as an RFC. So, some changes could still occur. Given the late stage of the process, it is unlikely it will change that much, but be aware that some changes could…
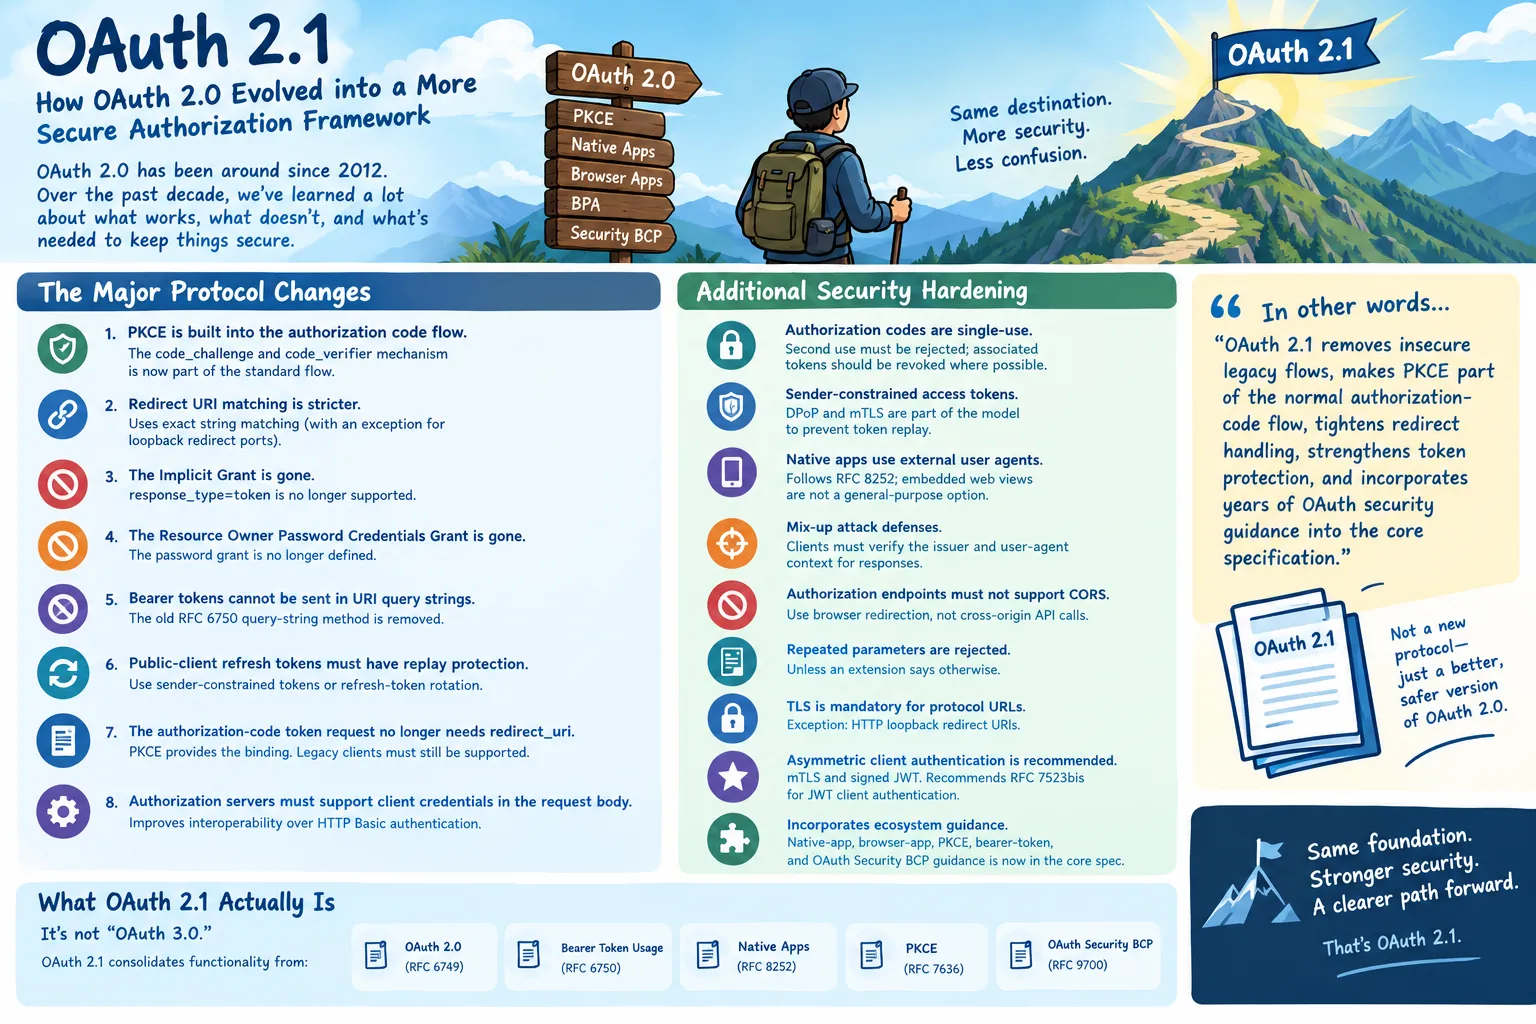
Read article: OAuth 2.1: How OAuth 2.0 Evolved into a More Secure Authorization FrameworkWe have spent decades building systems that ask people to prove who they are.
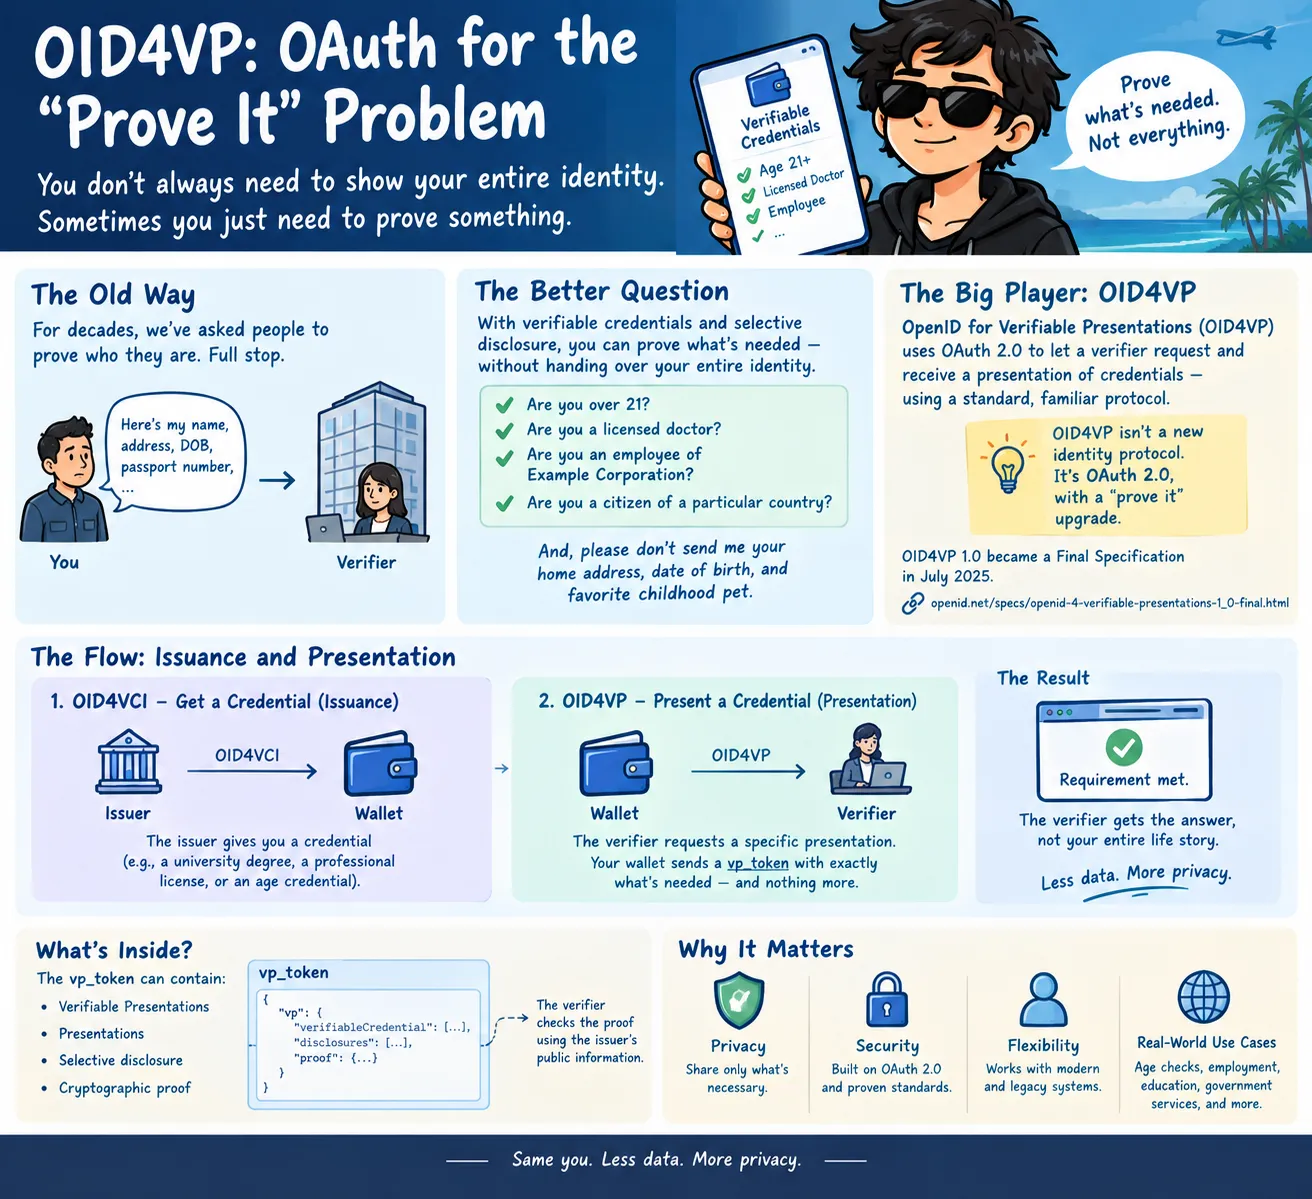
Read article: OID4VP: OAuth2 for the “Prove It” ProblemFor all the excitement around Verifiable Credentials, there is a rather mundane problem hiding underneath the cryptography:
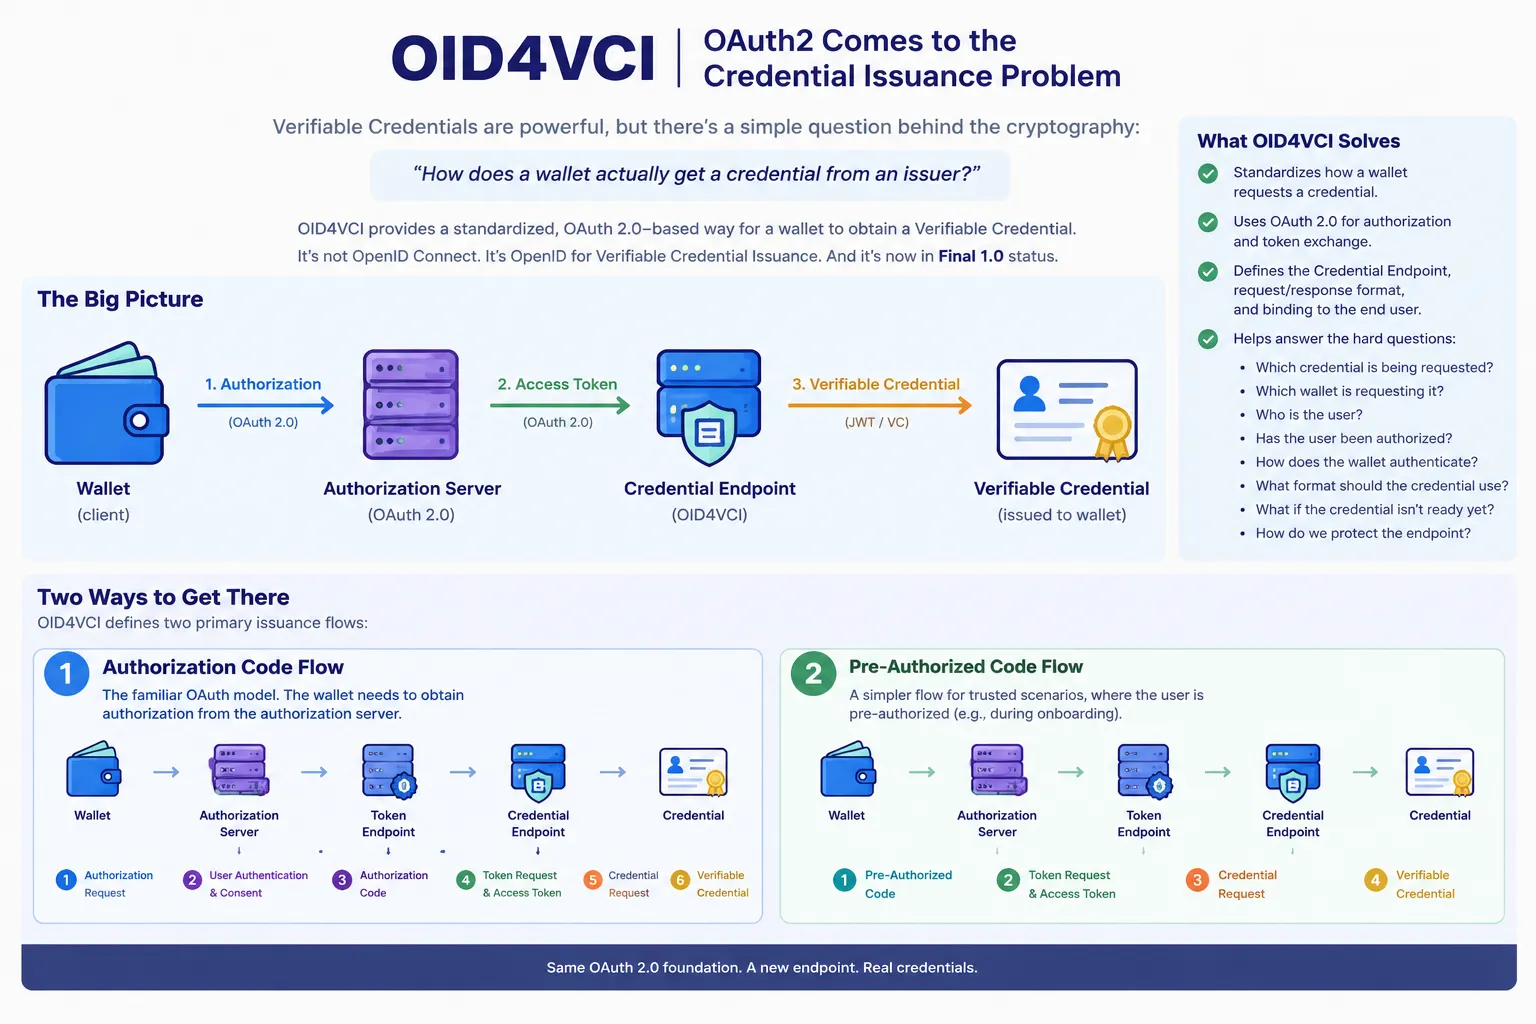
Read article: OID4VCI: OAuth2 Comes to the Credential Issuance ProblemThe Model Context Protocol, or MCP, has quickly become one of the most important pieces of infrastructure in the emerging Agentic AI ecosystem.
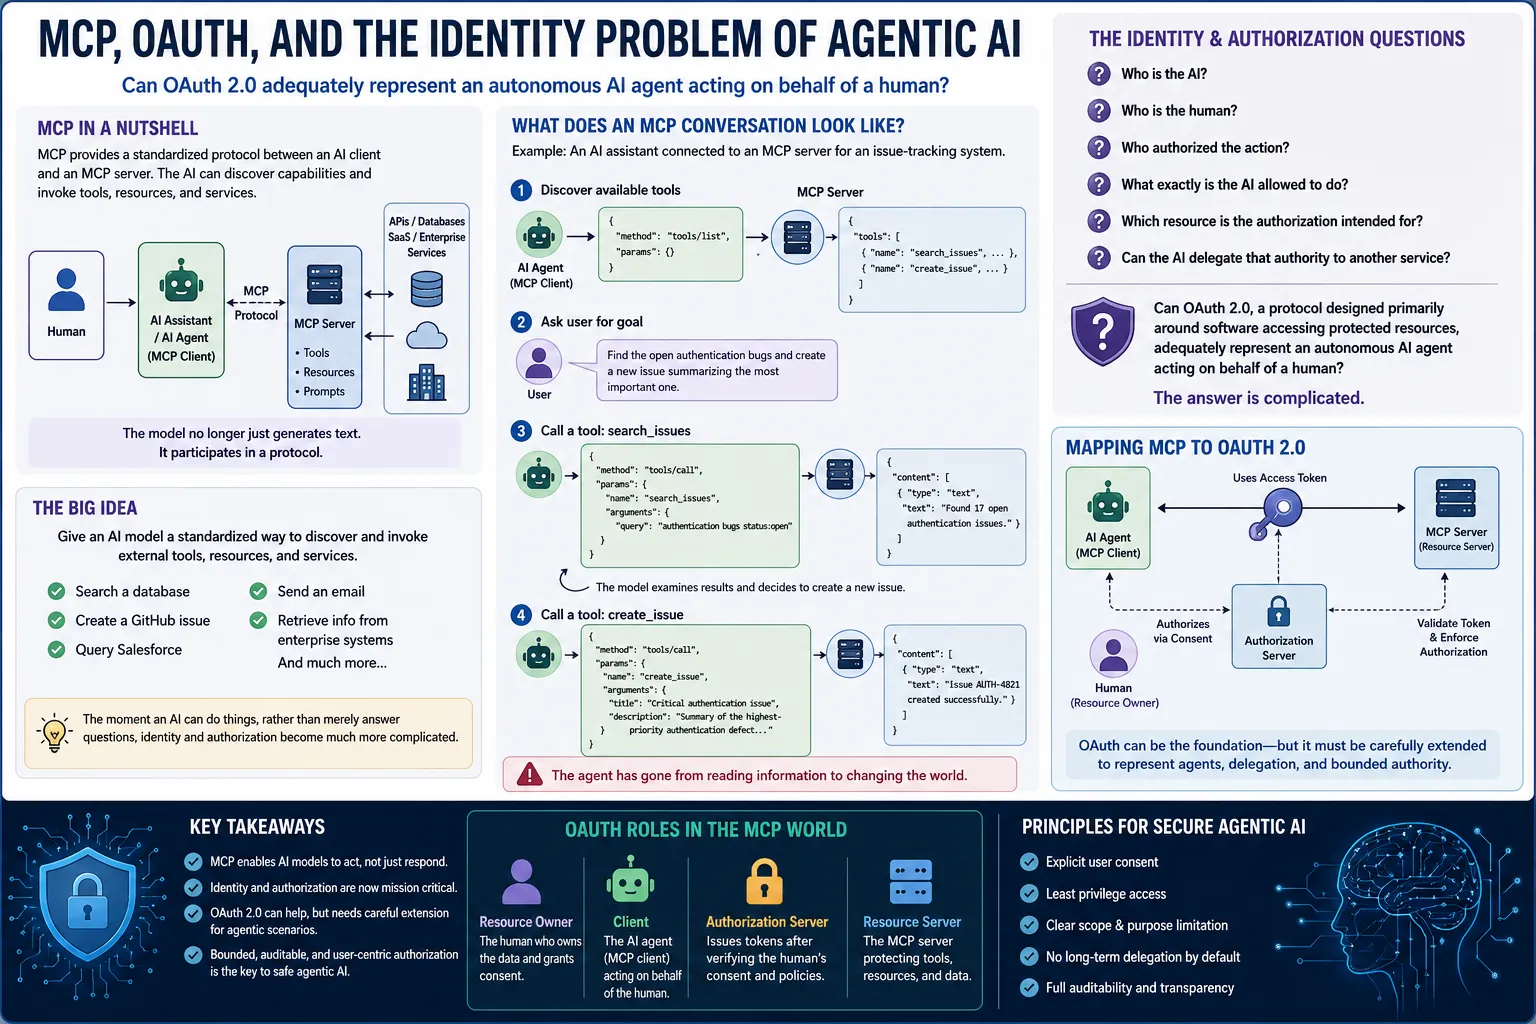
Read article: Model Context Protocol: MCP, OAuth2, and the Identity Problem of Agentic AIDelegation is a concept that has always fascinated me in the identity space. It enables secure identity propagation with tokens (assertions, tickets, etc) being properly scoped. As functionality in my Identity Protocol Debugger has continued to evolve, I wanted to add a feature that would make it…
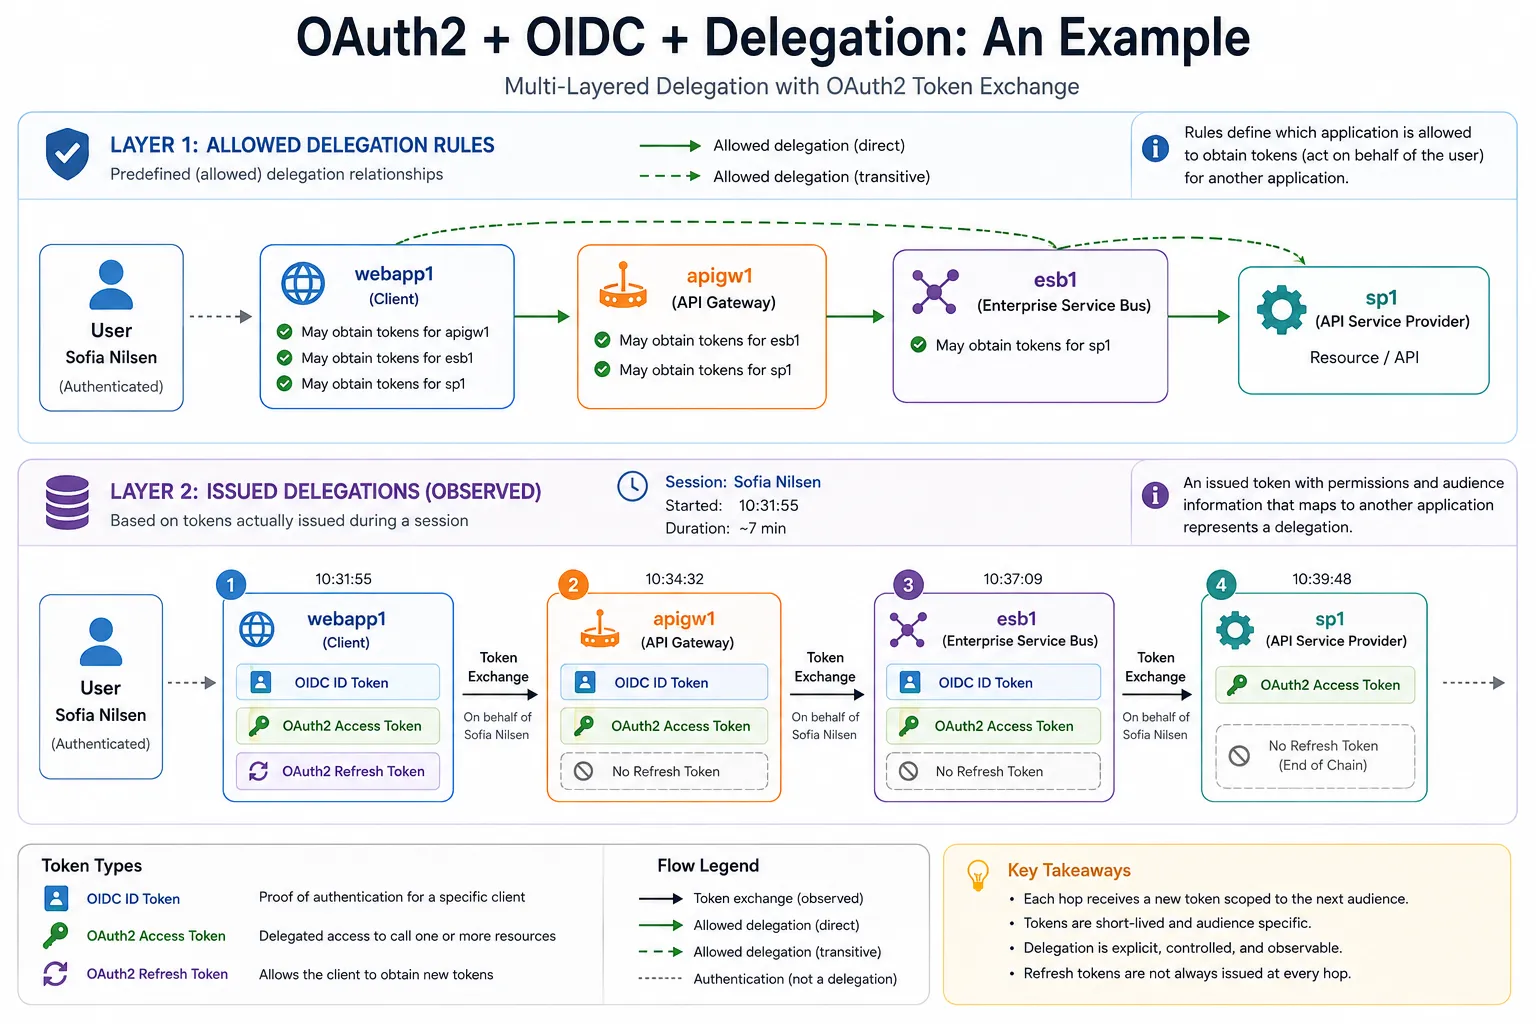
Read article: OAuth2 + OIDC + Delegation: An example