Supply Chain Security
5 articles tagged Supply Chain Security.
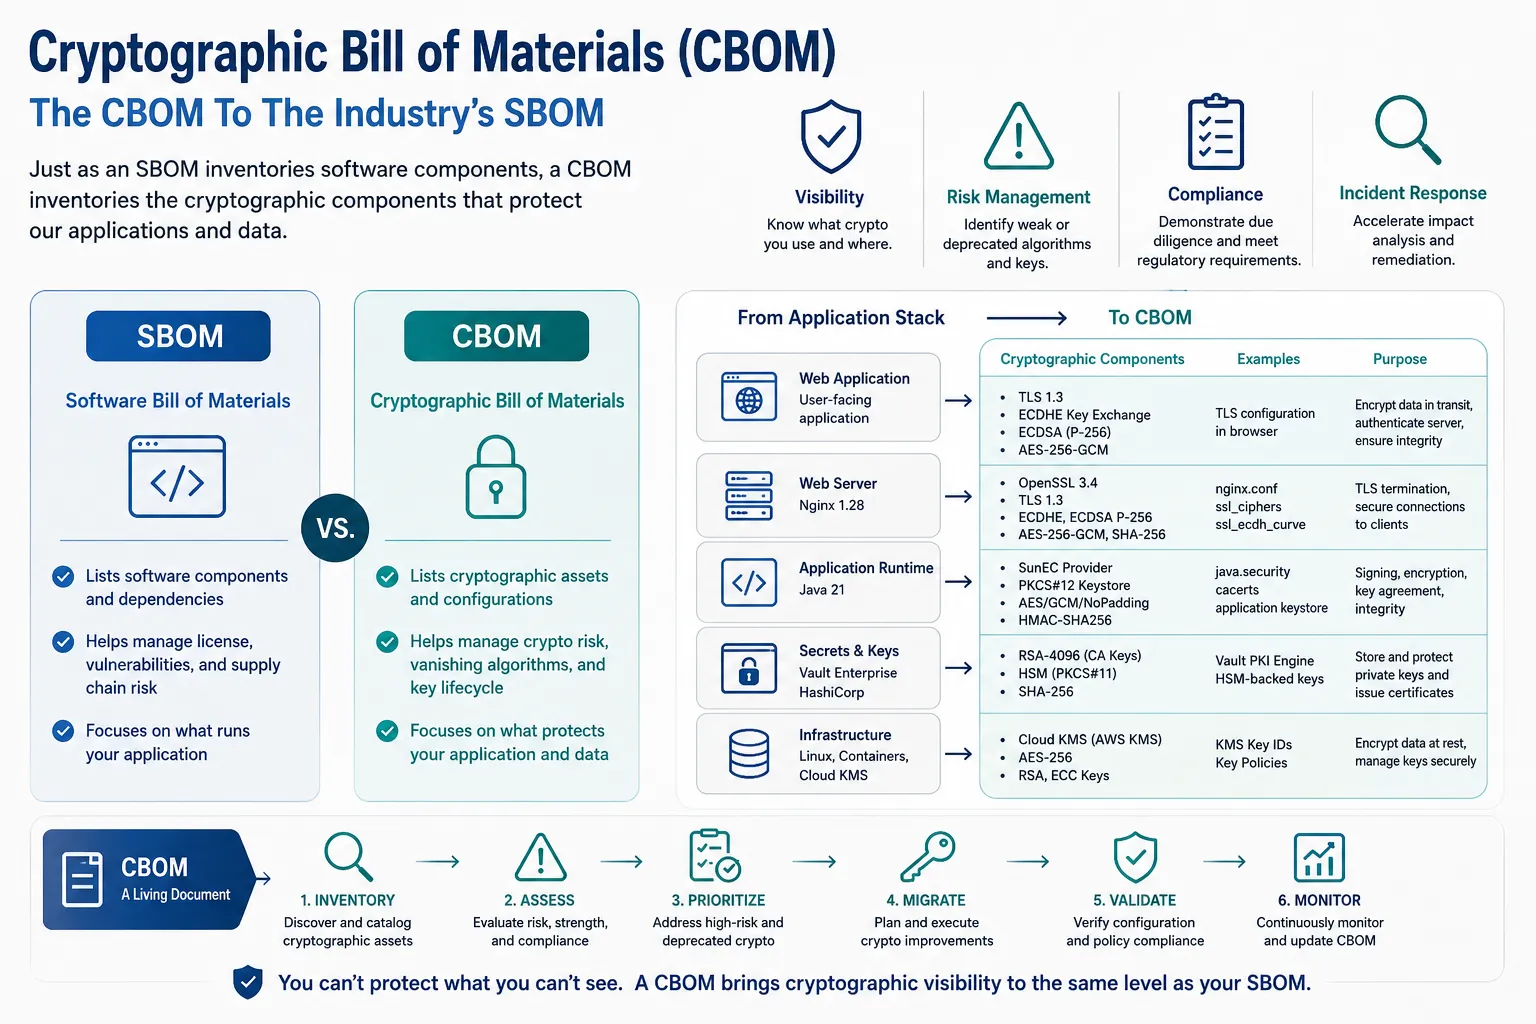
Cryptographic Bill of Materials: The CBOM To The Industry’s SBOM
A Cryptographic Bill of Materials (CBOM) is exactly what it sounds like: an inventory of every cryptographic component used throughout an organization. If a Software Bill of Materials (SBOM) tells you what software you have, a CBOM tells you how that software is protected.
Read article: Cryptographic Bill of Materials: The CBOM To The Industry’s SBOM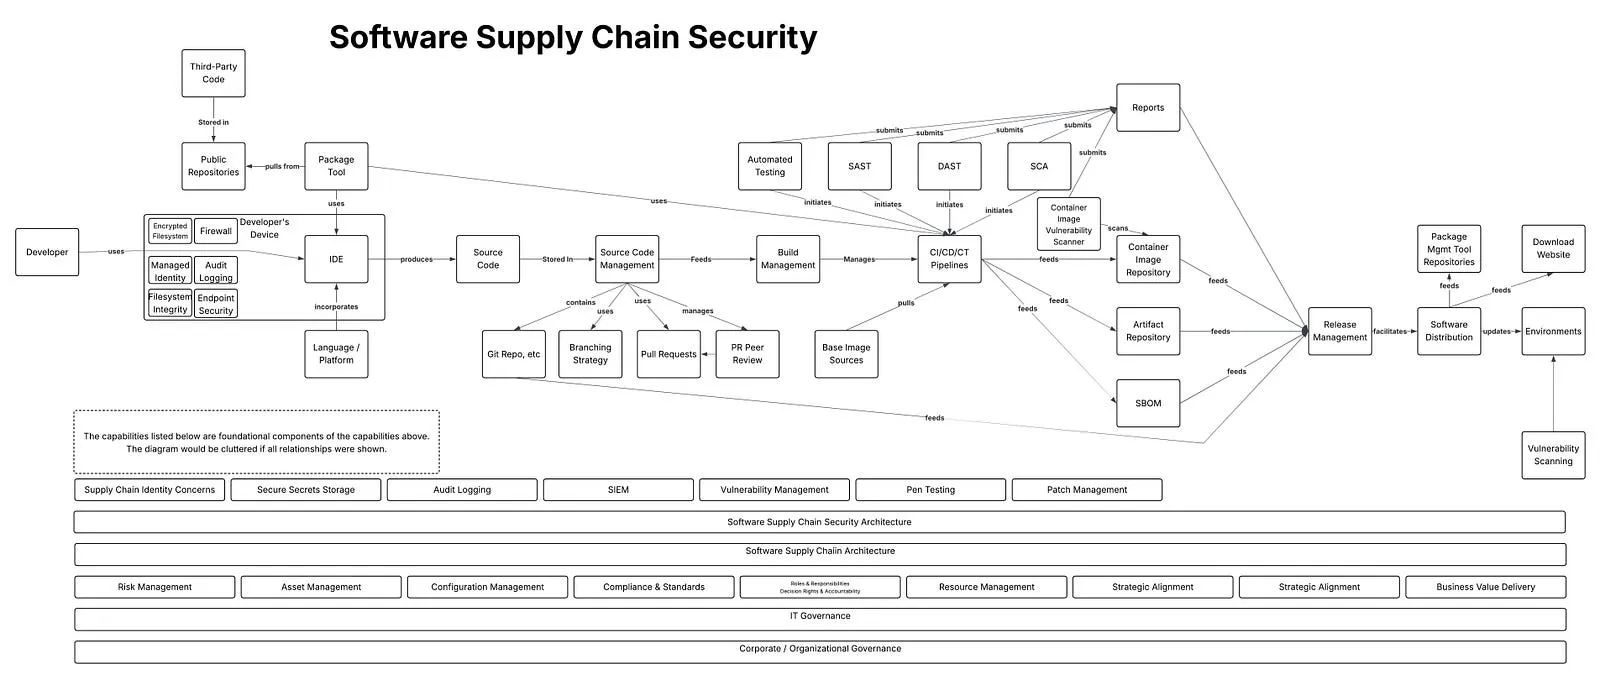
SOFTWARE SUPPLY CHAIN SECURITY: CI/CD/CT PIPELINES AND SECURITY TOOLS — PART 2
This is part two of a two part blog post on Software Supply Chain Security. If you haven’t read Part 1 yet, starting there is recommended.
Read article: SOFTWARE SUPPLY CHAIN SECURITY: CI/CD/CT PIPELINES AND SECURITY TOOLS — PART 2SOFTWARE SUPPLY CHAIN SECURITY: CI/CD/CT PIPELINES AND SECURITY TOOLS — PART 1
The DevOps movement of the last decade more-or-less led to the DevSecOps movement of this decade. This focus on automation to create efficient, end-to-end software publishing pipelines combined with incidents like the SolarWinds Hack in 2020 and the recent ‘S1ngularity’ attack on the NPM ecosystem…
Read article: SOFTWARE SUPPLY CHAIN SECURITY: CI/CD/CT PIPELINES AND SECURITY TOOLS — PART 1
What is Authorization?
In a previous post, I gave a definition of Authentication. In this post, we’re going to explore authorization, which is typically the next step in the processing pipeline after authentication. The concepts described here can apply equally to traditional web applications, SPA apps, mobile apps,…
Read article: What is Authorization?