Firebase API Keys: Got a Callback From A Potential Client
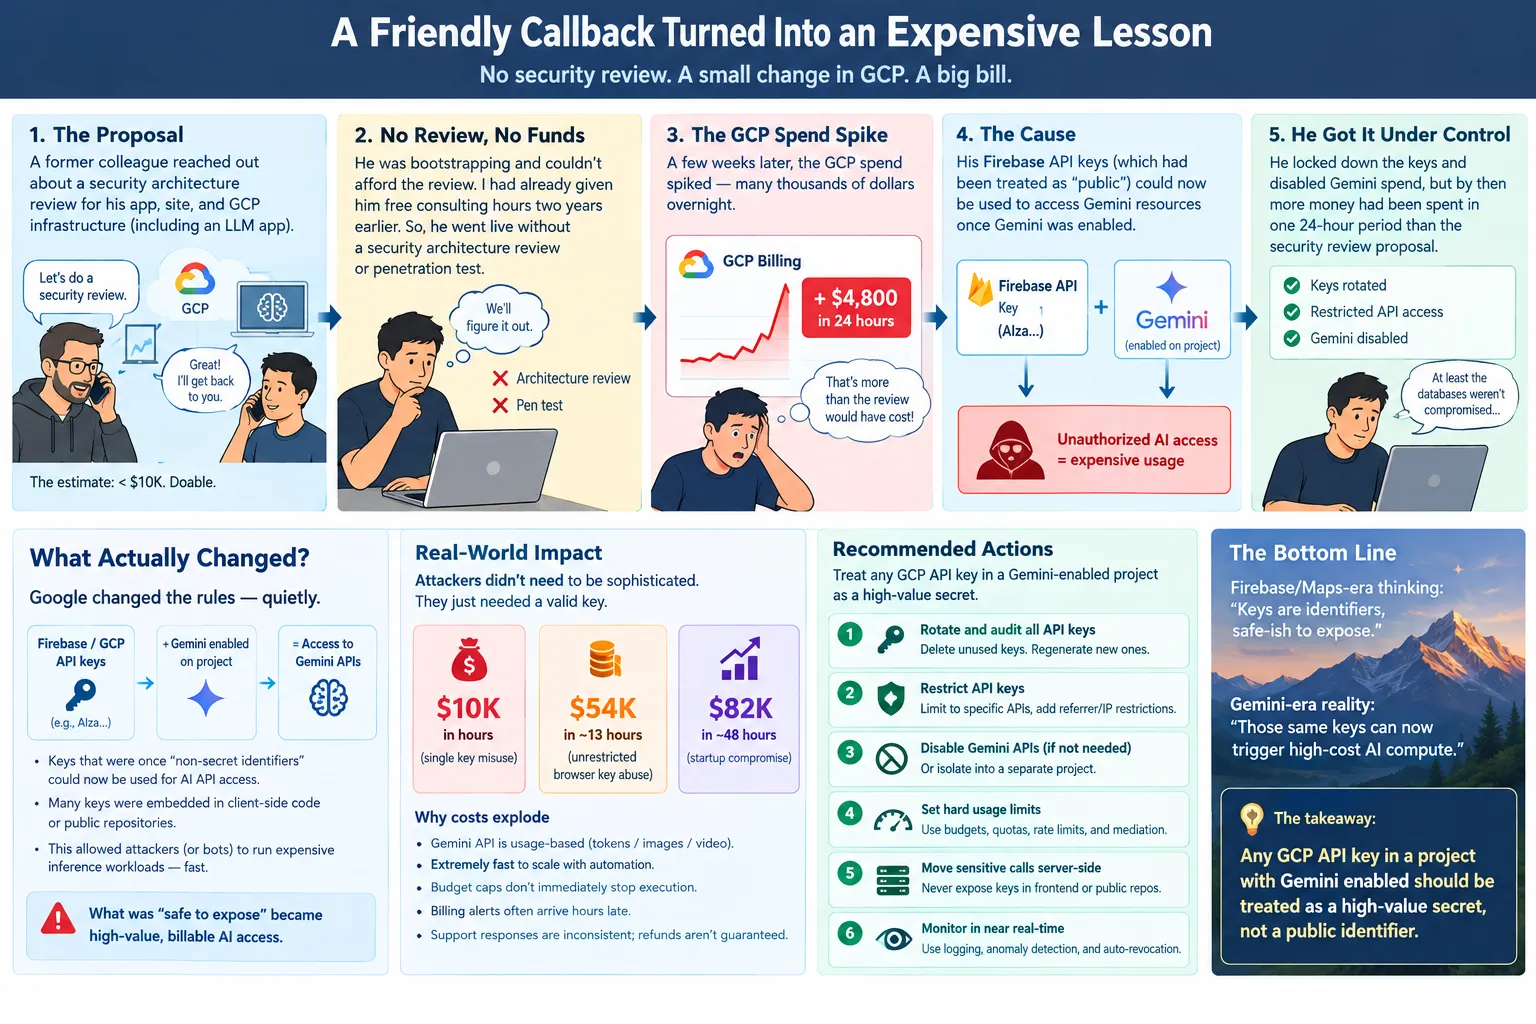
I originally wrote this post about six months ago. Variations of this story have been published many times this year.
Read article: Firebase API Keys: Got a Callback From A Potential Client32 articles tagged Authorization.
I originally wrote this post about six months ago. Variations of this story have been published many times this year.
Read article: Firebase API Keys: Got a Callback From A Potential ClientOAuth2 has been around long enough that it is easy to forget just how much machinery has accumulated around it.
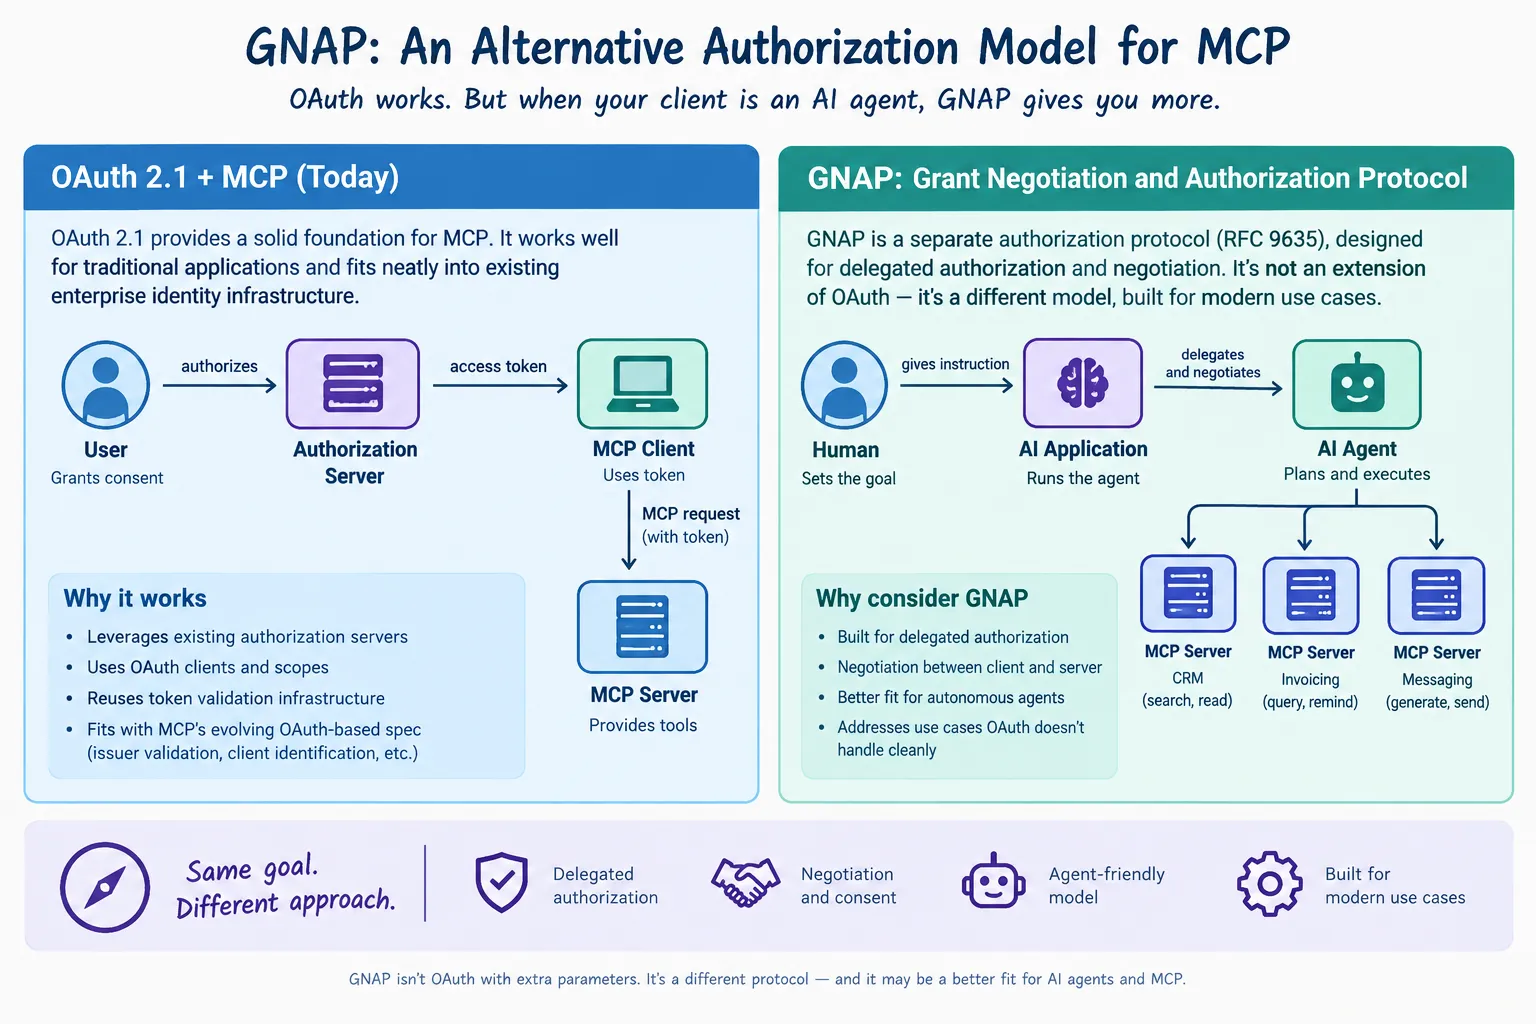
Read article: GNAP: An Alternative Authorization Model for MCPOAuth2 has a fairly straightforward model. A client authenticates to an authorization server, obtains an access token, and uses that token to access a protected resource.
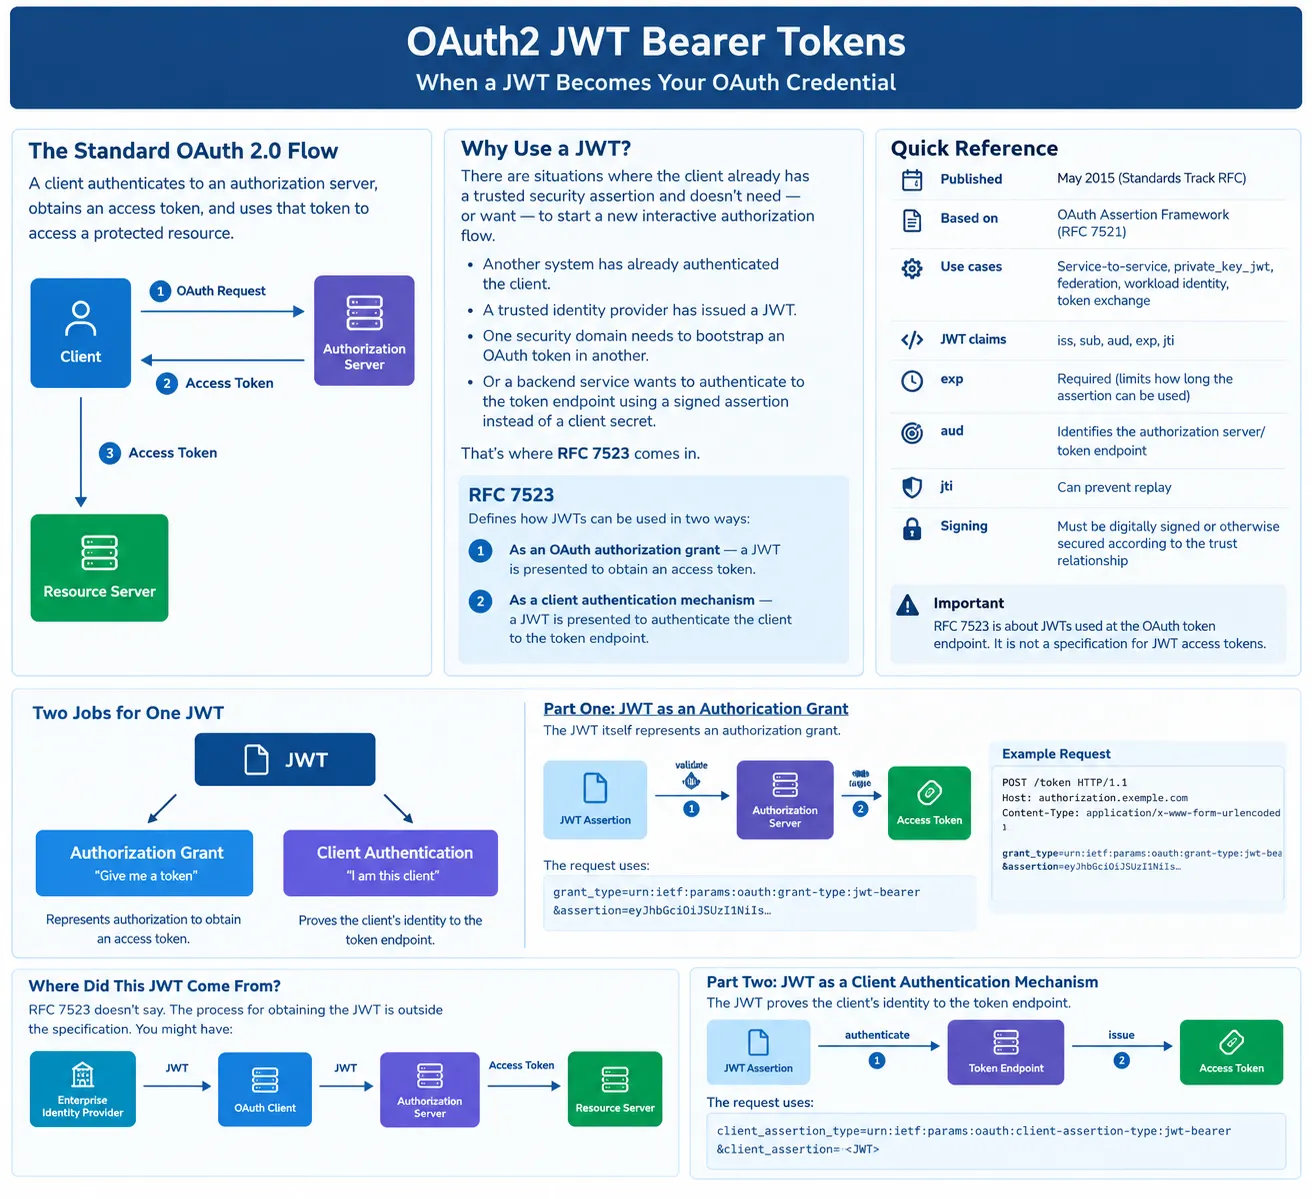
Read article: OAuth2 JWT Bearer Tokens (RFC-7523): When a JWT Becomes Your OAuth2 CredentialOAuth2 was designed around the assumption that the client can open a browser.
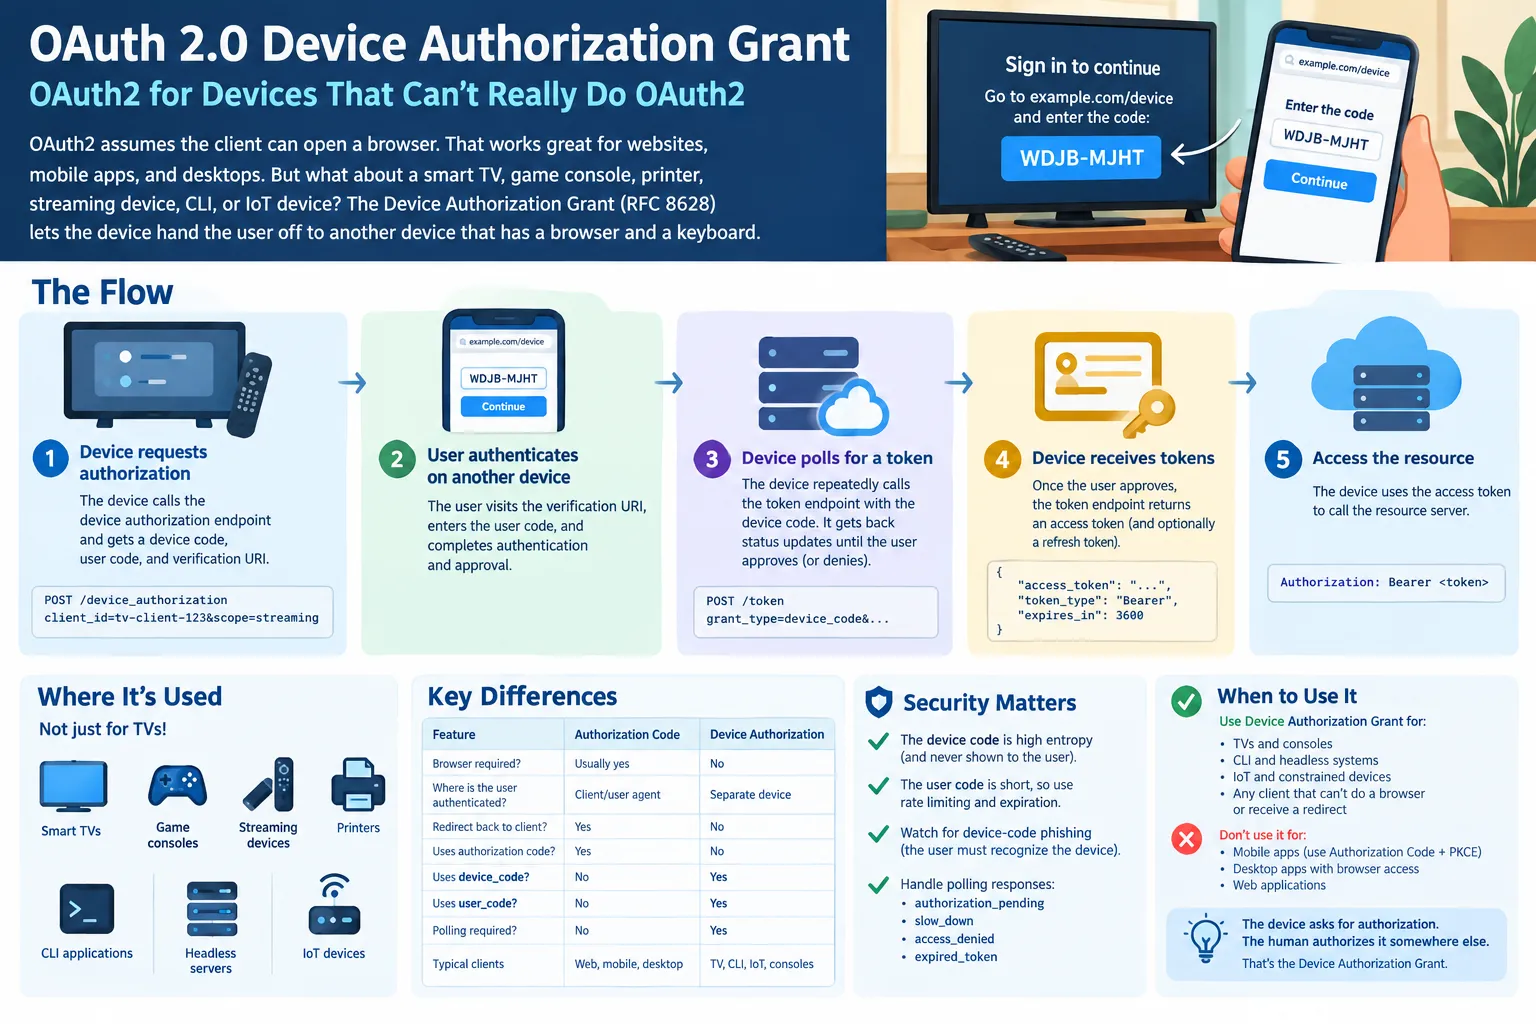
Read article: OAuth2 Device Authorization Grant: OAuth2 for Devices That Can’t Really Do OAuth2Disclaimer: This article was written in Q3,2026. It is current as of that date. The OAuth 2.1 draft proposals have not yet been published as an RFC. So, some changes could still occur. Given the late stage of the process, it is unlikely it will change that much, but be aware that some changes could…
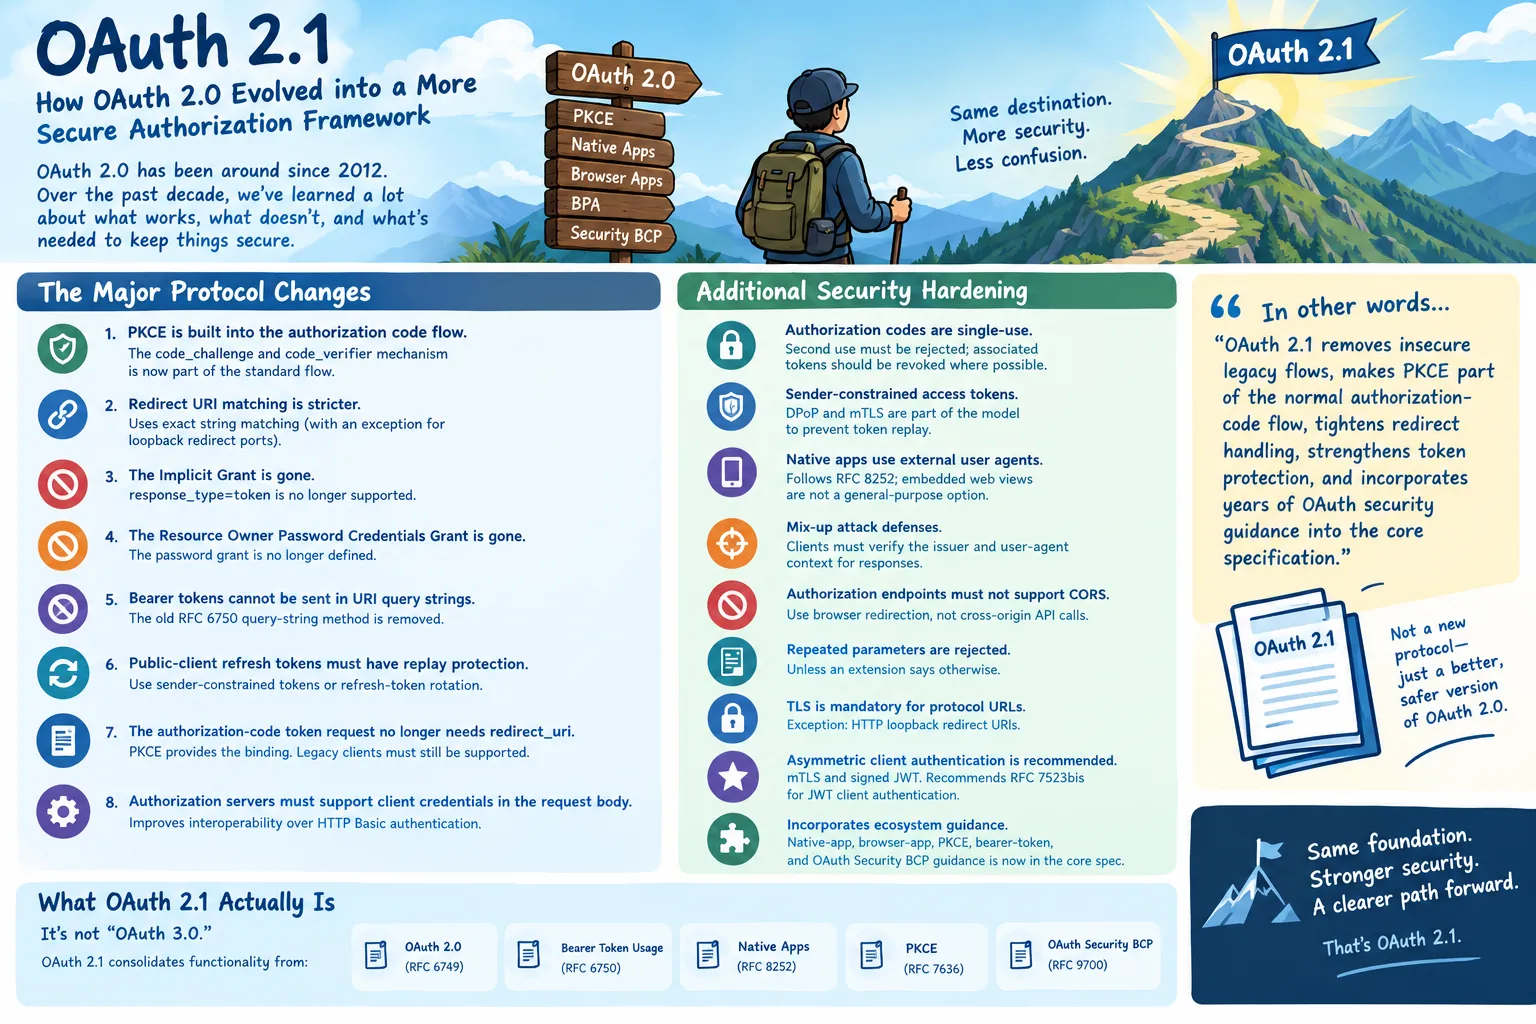
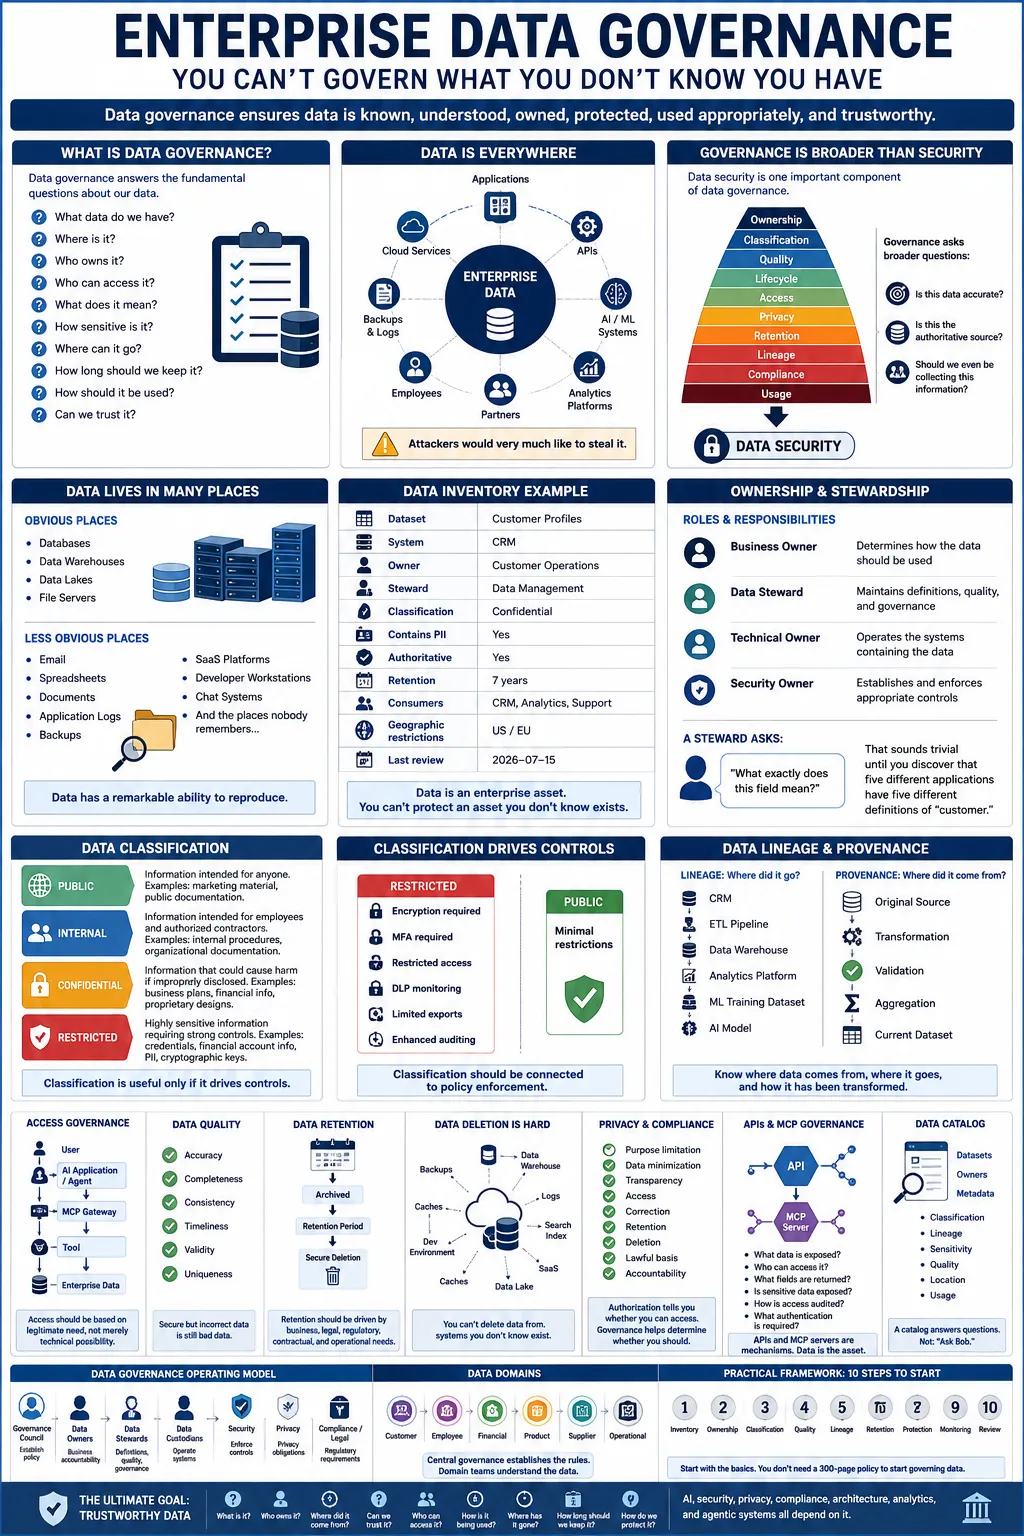
Read article: OAuth 2.1: How OAuth 2.0 Evolved into a More Secure Authorization FrameworkThere are few phrases in enterprise IT capable of making a room become noticeably quieter than, “We need to talk about data governance.”
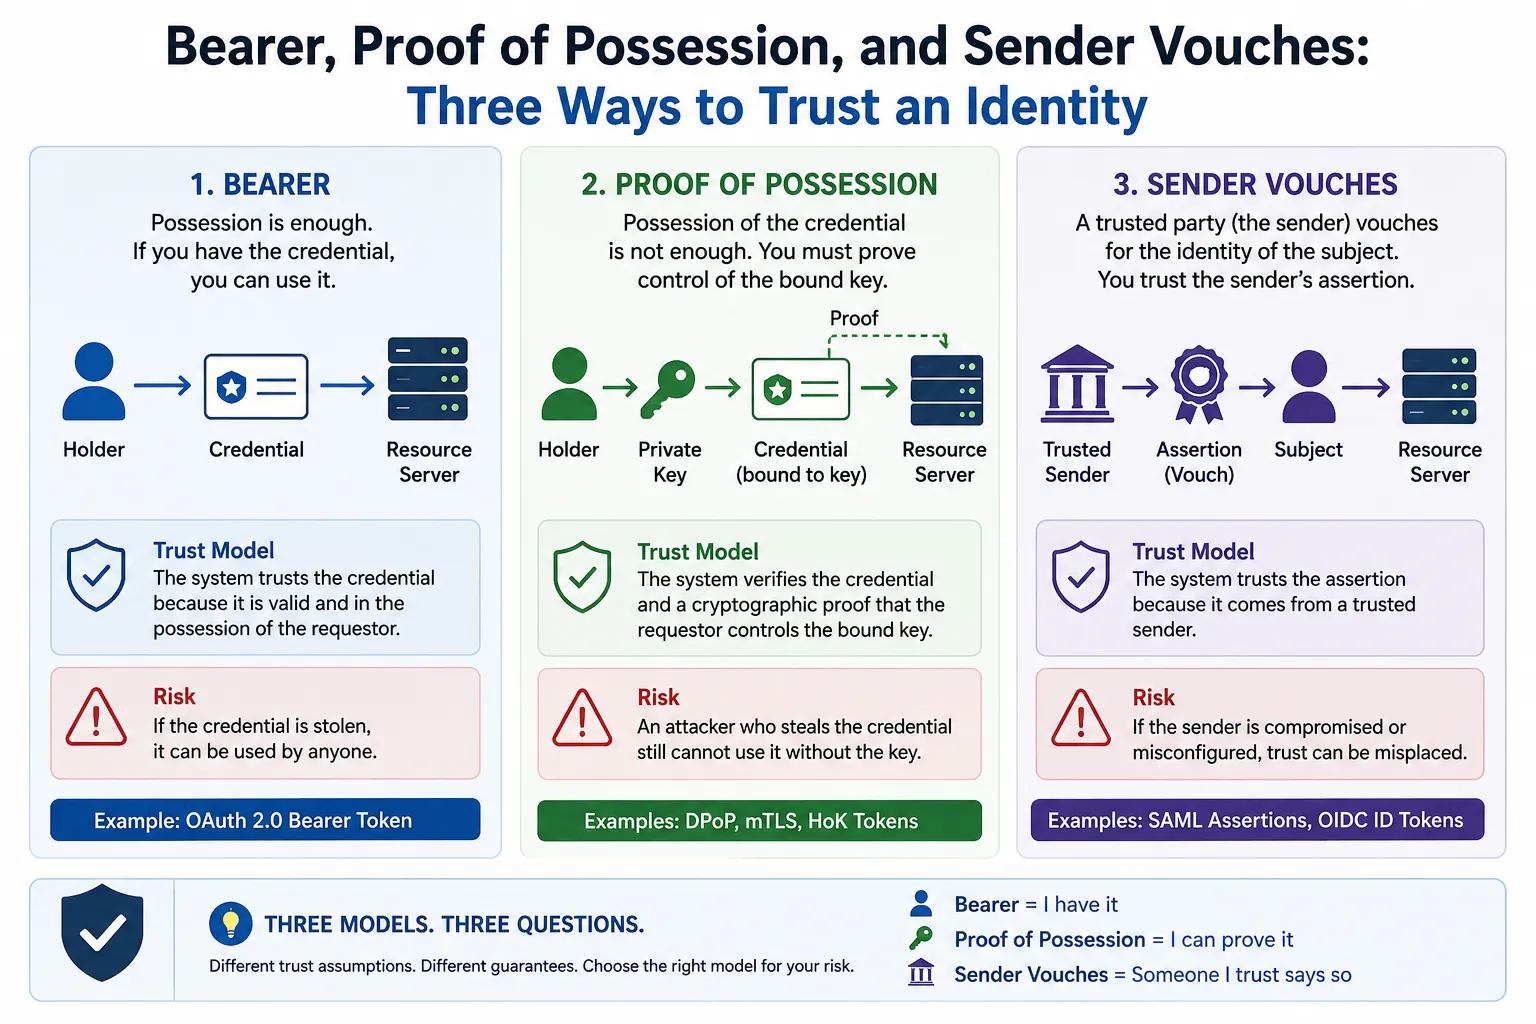
Read article: Enterprise Data Governance: You Can’t Govern What You Don’t Know You HaveOne of the most fundamental questions in any identity or authorization system is how does the system know that the party presenting a credential is actually entitled to use it?
Read article: Bearer, Proof of Possession, and Sender Vouches: Three Ways to Trust an IdentityThere is a wonderful phrase that gets tossed around in corporate IT meetings.
Read article: Risk Management: Or How Corporate IT Learned to Fear Everything Except the Things That Actually…Authentication is one of the most fundamental concepts in application security. Most developers spend considerable time designing how authenticated users are represented, authorized, and managed. Surprisingly, much less attention is given to the opposite state of users who have not authenticated at…
Read article: Understanding Unauthenticated Traffic: How Applications and APIs Represent The Unauthenticated UserFor decades, organizations have focused on keeping attackers out. Firewalls, antivirus software, intrusion detection systems, IAM solutions, and the like all serve a common purpose to prevent unauthorized access. However, many security incidents do not begin with an external attacker breaking in.…
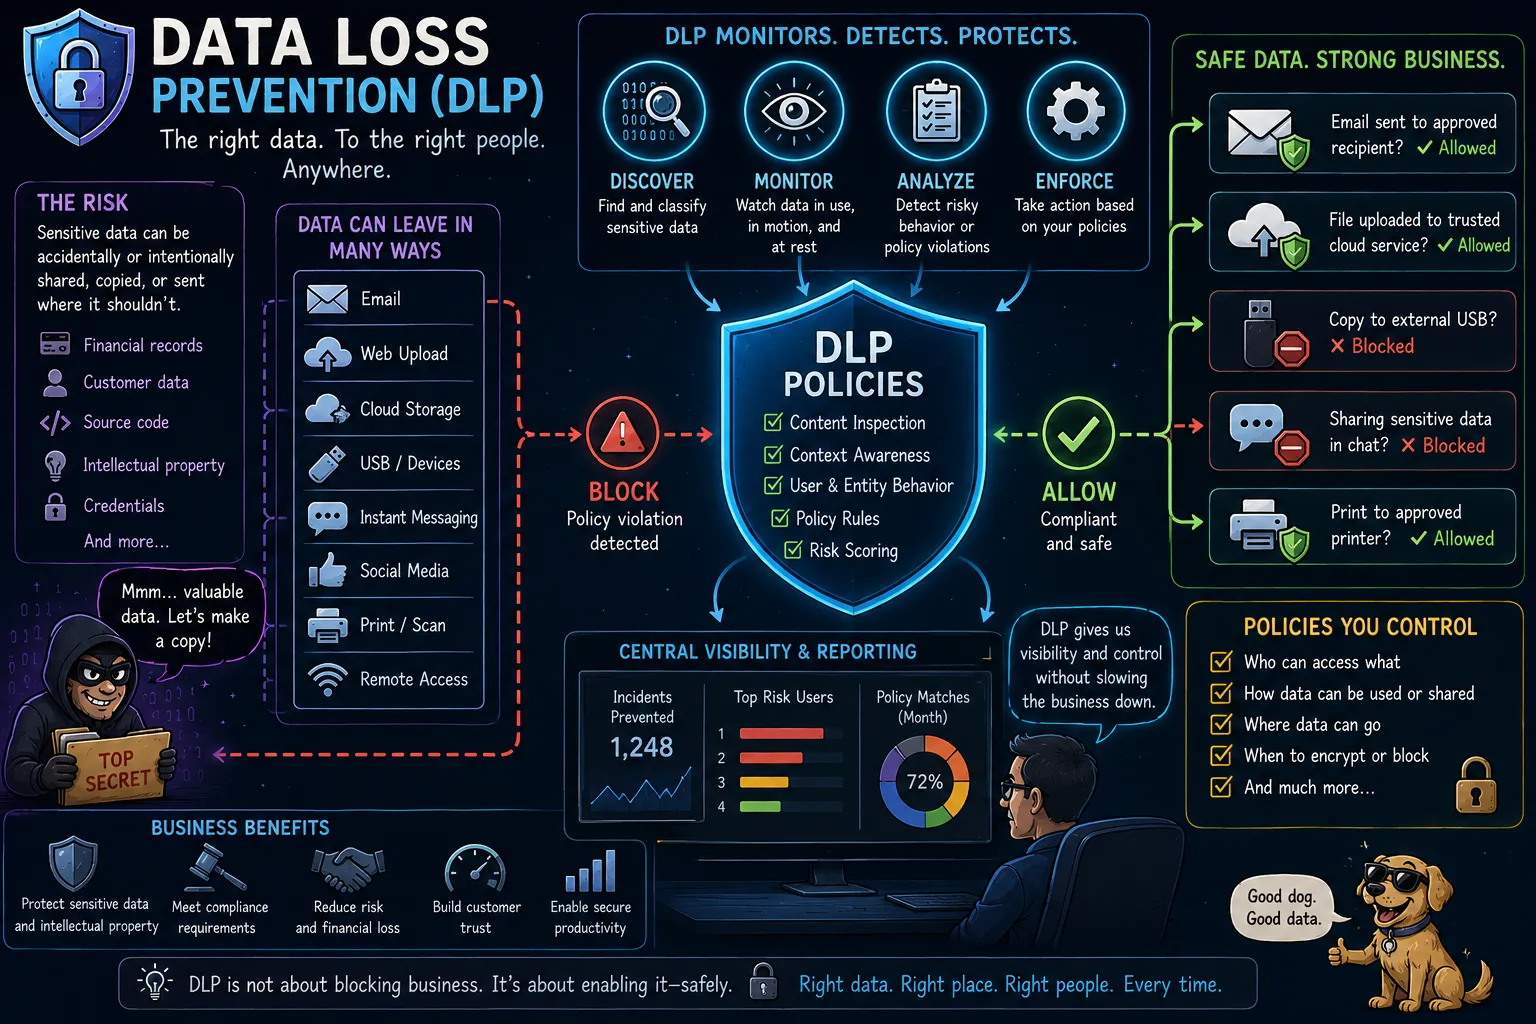
Read article: Data Loss Prevention (DLP): Keeping Your Organization’s Secrets from Walking Out the Door