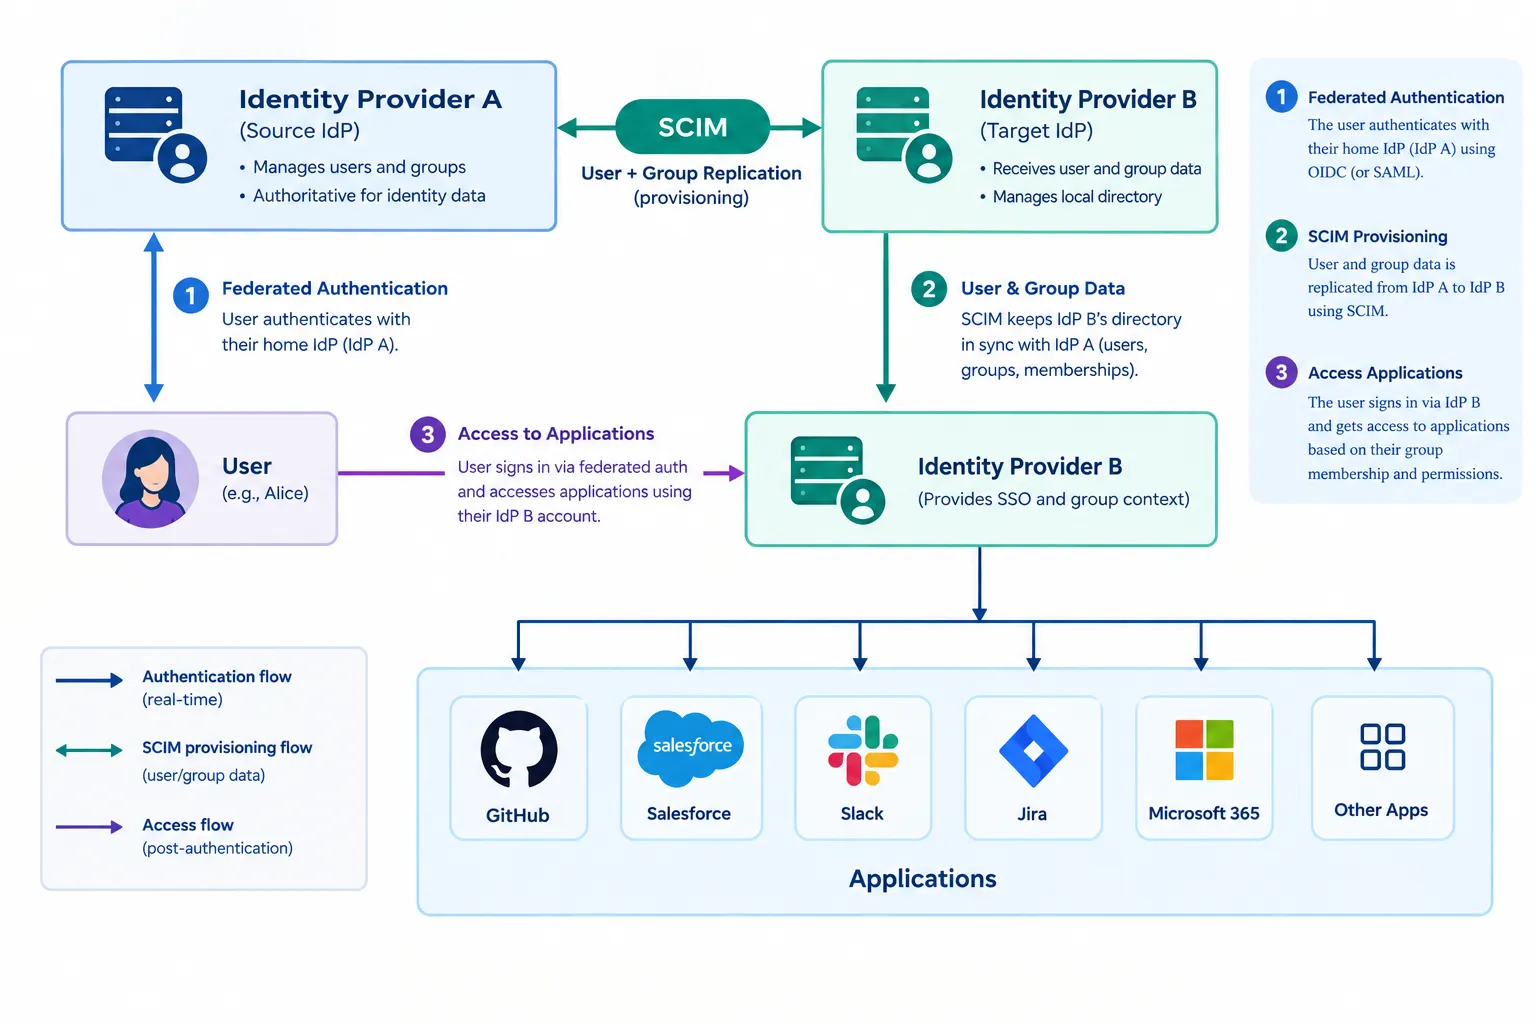
SCIM: System for Cross-Domain Identity Management
There is a glamorous side to identity management, if any of this actually constitutes glamorous.
Read article: SCIM: System for Cross-Domain Identity Management17 articles tagged Identity & Access Management.
There is a glamorous side to identity management, if any of this actually constitutes glamorous.
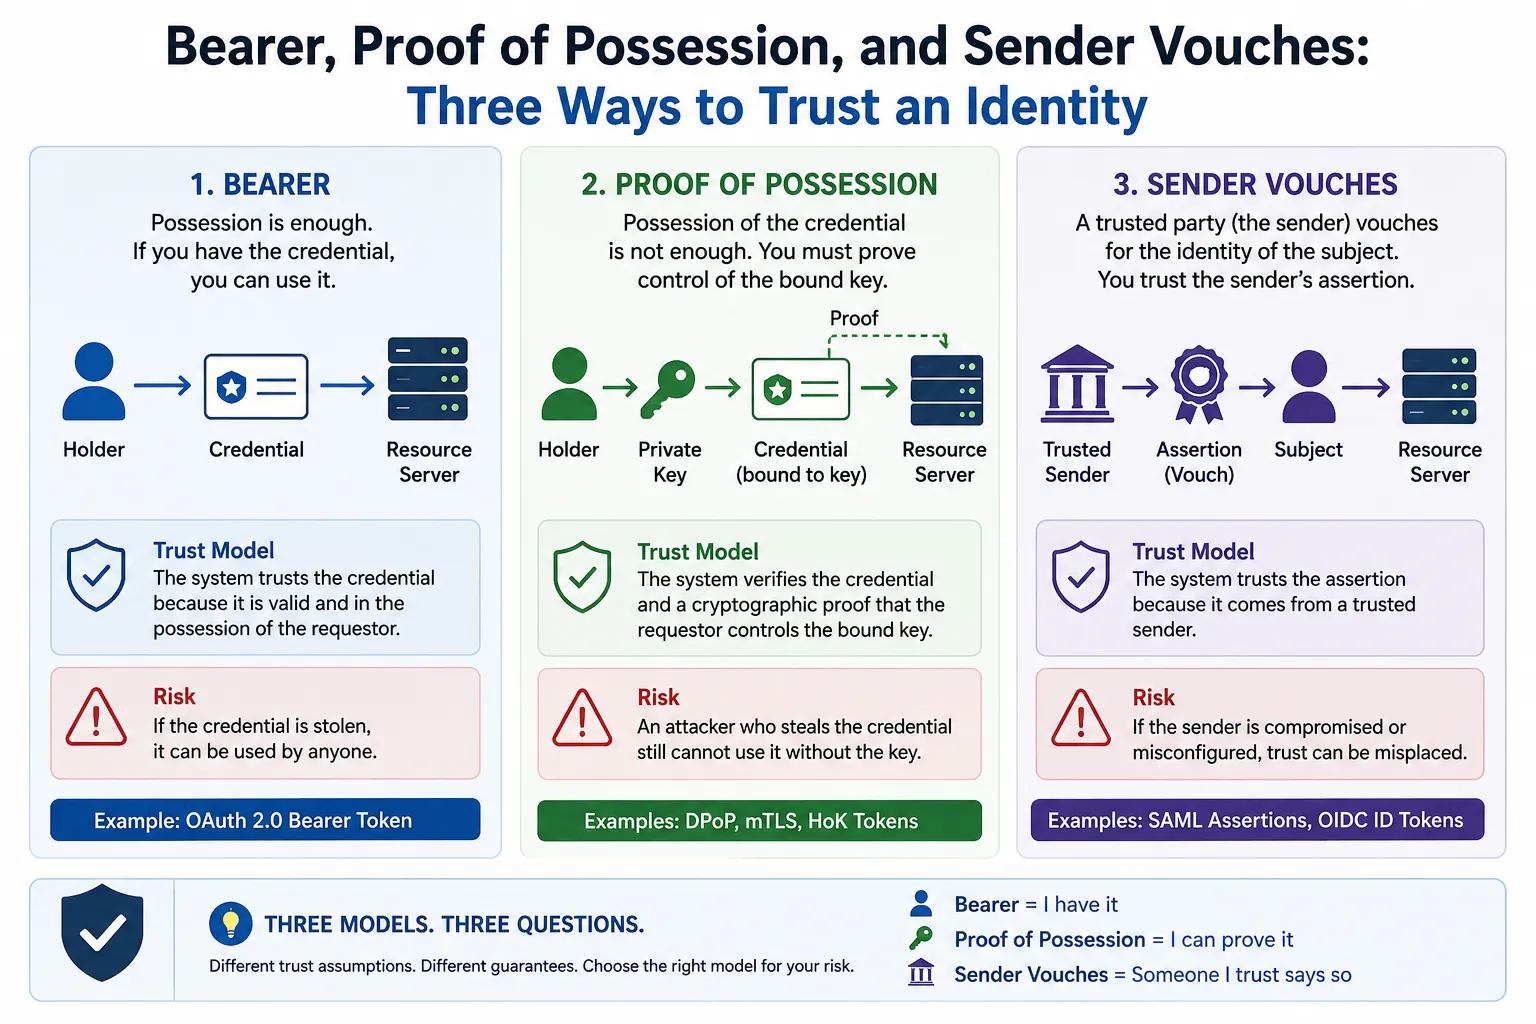
Read article: SCIM: System for Cross-Domain Identity ManagementOne of the most fundamental questions in any identity or authorization system is how does the system know that the party presenting a credential is actually entitled to use it?
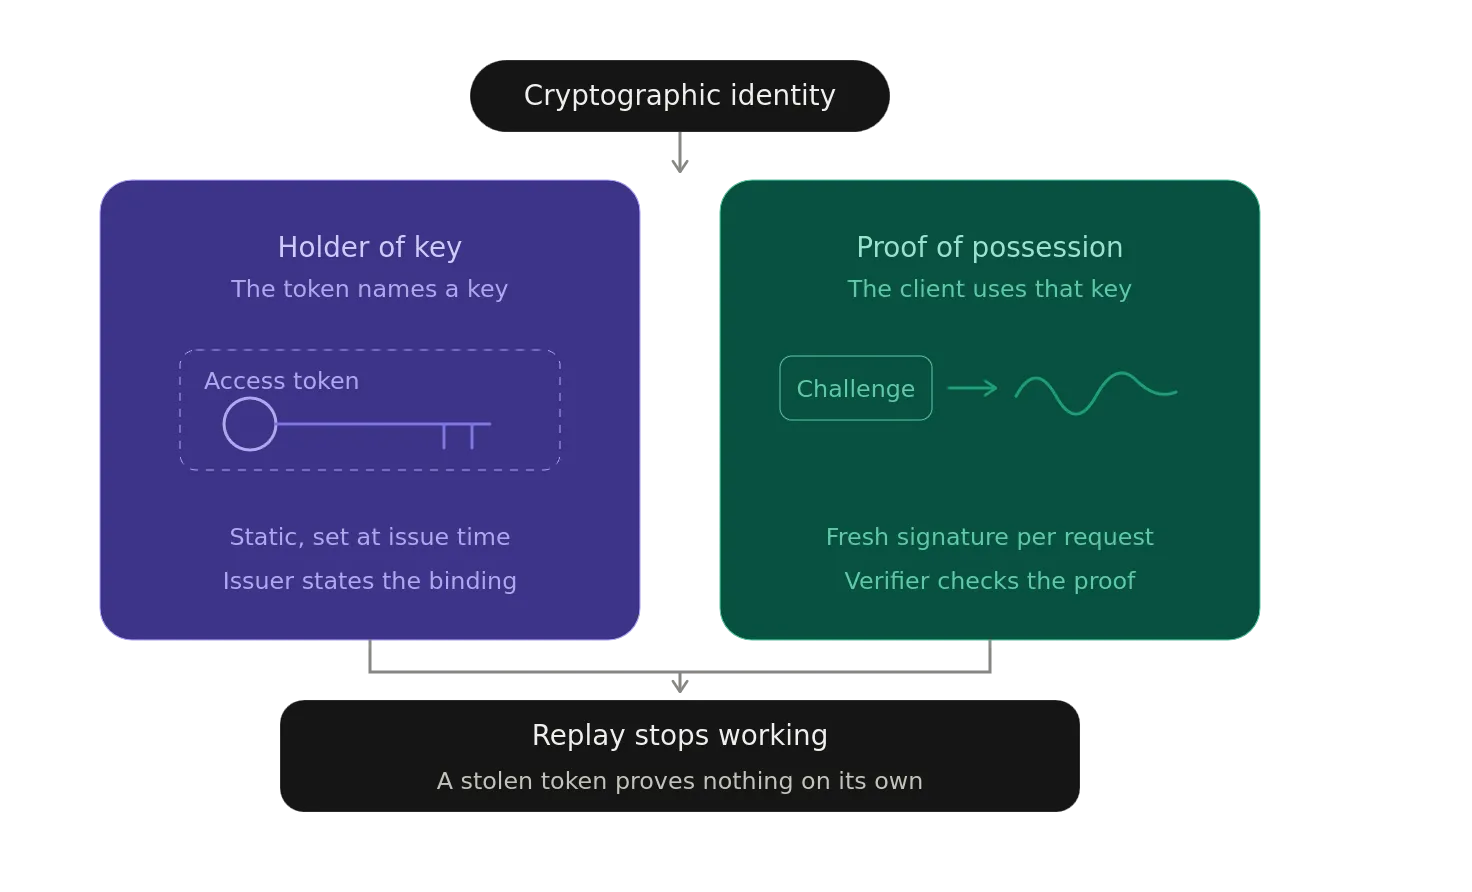
Read article: Bearer, Proof of Possession, and Sender Vouches: Three Ways to Trust an IdentityFor years, identity protocols have used phrases such as Holder of Key, Proof of Possession, Key Binding, and Bearer almost interchangeably.
Read article: Holder of Key vs. Proof of Possession: Two Sides of Cryptographic IdentityI started thinking about this post a while back when I saw a former colleague’s Medium profile still listed as following mine. He died in the early days of covid. A quick check showed that his LinkedIn profile seems to have disappeared — not sure how that works. It was still there a few years ago.
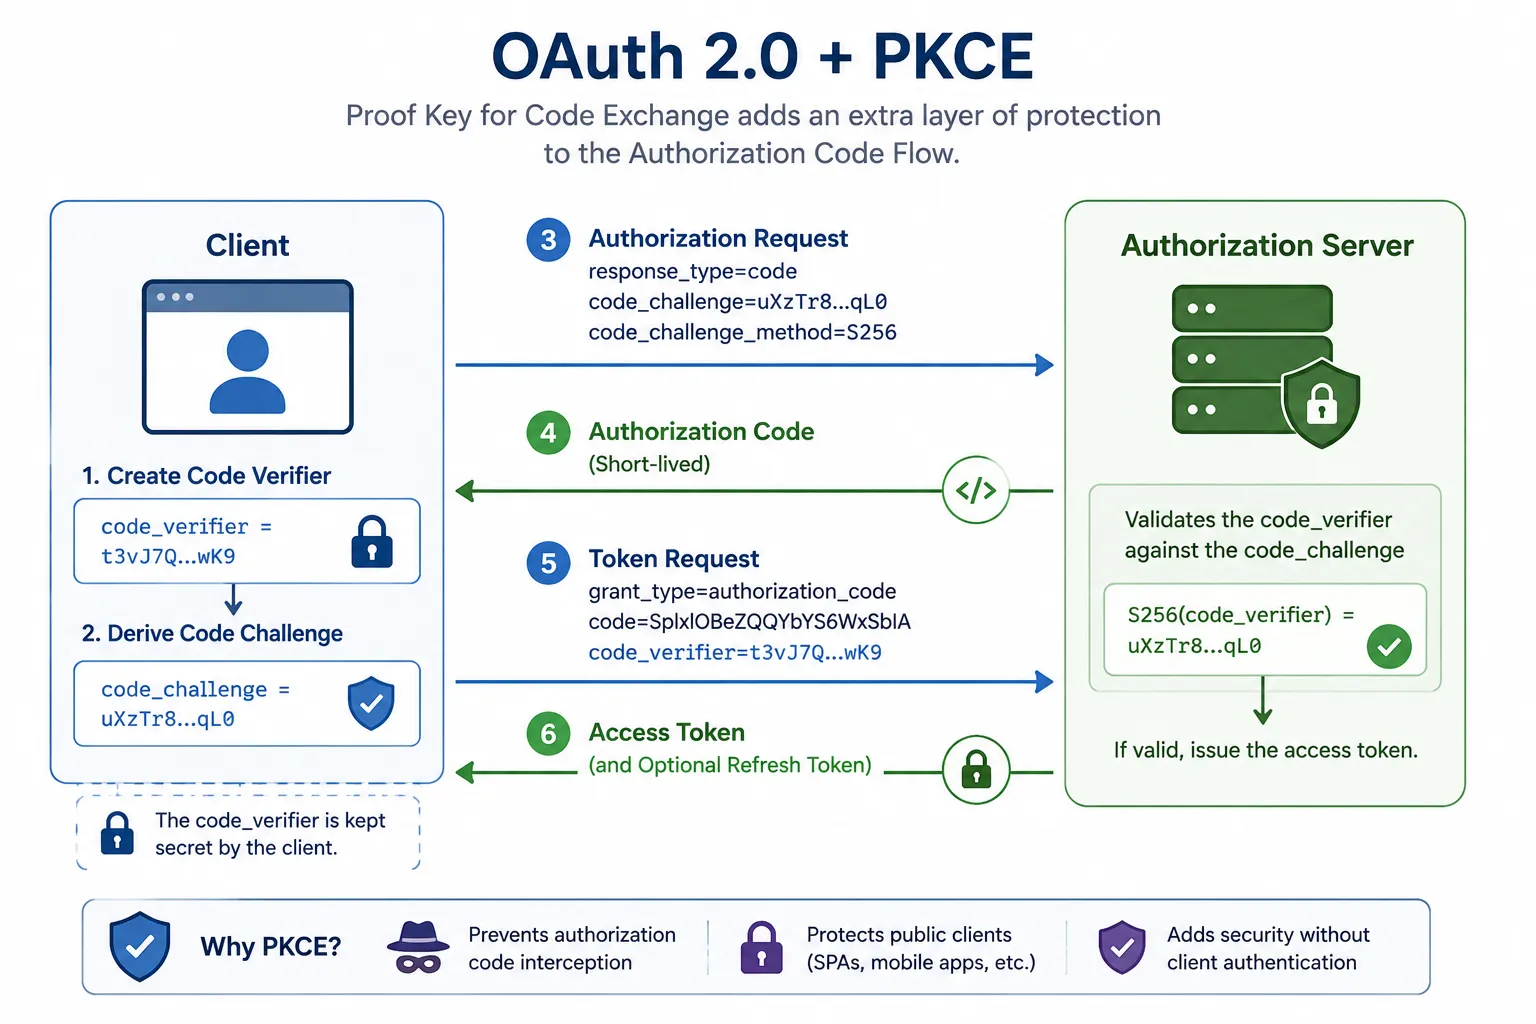
Read article: The Digital Dead: Existence Beyond Death OnlineOne of the biggest misconceptions about OAuth2 is that it is a single protocol. In reality, OAuth2 has evolved considerably over the years as new attack vectors have been discovered and new security mechanisms introduced. One of the most significant of these improvements is Proof Key for Code…
Read article: PKCE: Proof Key for Code ExchangeFor anyone who has been paying attention, this blog post has been a long-time coming for multiple reasons. First, this is my first blog post in a couple of years — I’ve been heads down on a couple of projects for awhile now. This is literally the first time I’ve “come up for air” since the last…
Read article: RFC 9068: A JWT-Based OAuth2 Access Token Format Standard