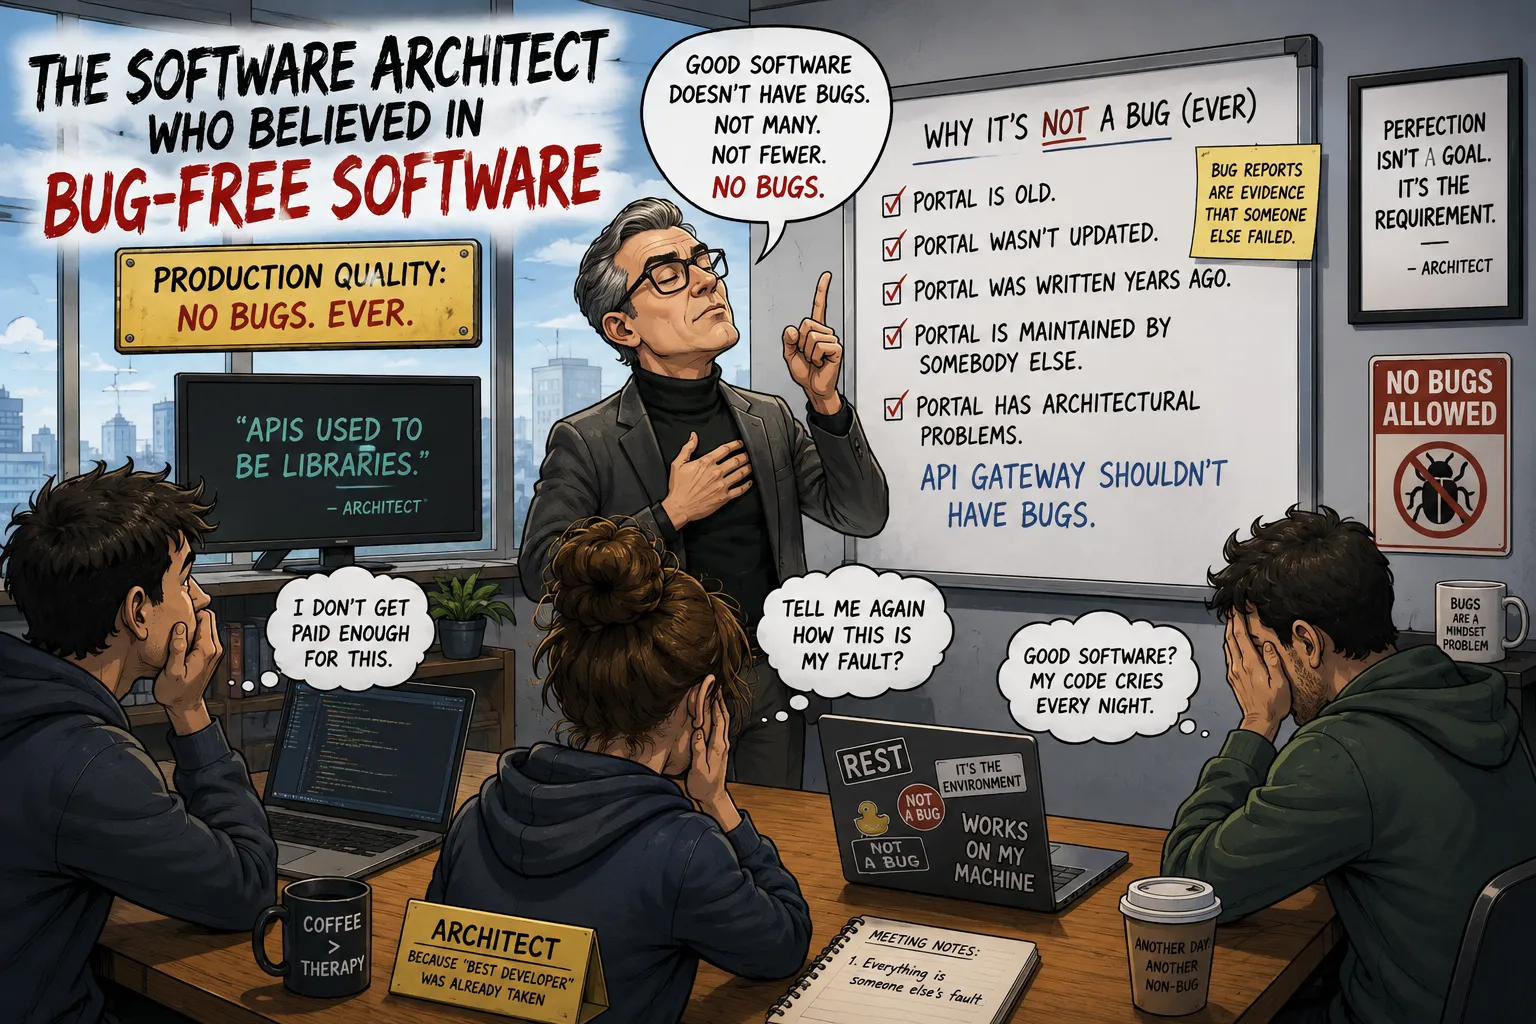
The Software Architect Who Believed in Bug-Free Software
I once worked with an architect who had a fascinating theory about software development.
Read article: The Software Architect Who Believed in Bug-Free Software8 articles tagged Identity Providers.
I once worked with an architect who had a fascinating theory about software development.
Read article: The Software Architect Who Believed in Bug-Free SoftwareYour production environment should be isolated from your non-production environments. In fact, every application environment should be isolated from every other environment. Sounds simple in practice, but how does one accomplish this? Through a multi-layered isolation strategy:
Read article: Achieving Application Environment IsolationWhile researching an upcoming blog post about Kerberos and Mobile, I needed to understand how Identity Providers (like ADFS or Ping Federate) use Kerberos (and possibly Kerberos Delegation) to perform authentication via username and password. This blog post captures what I found for ADFS.
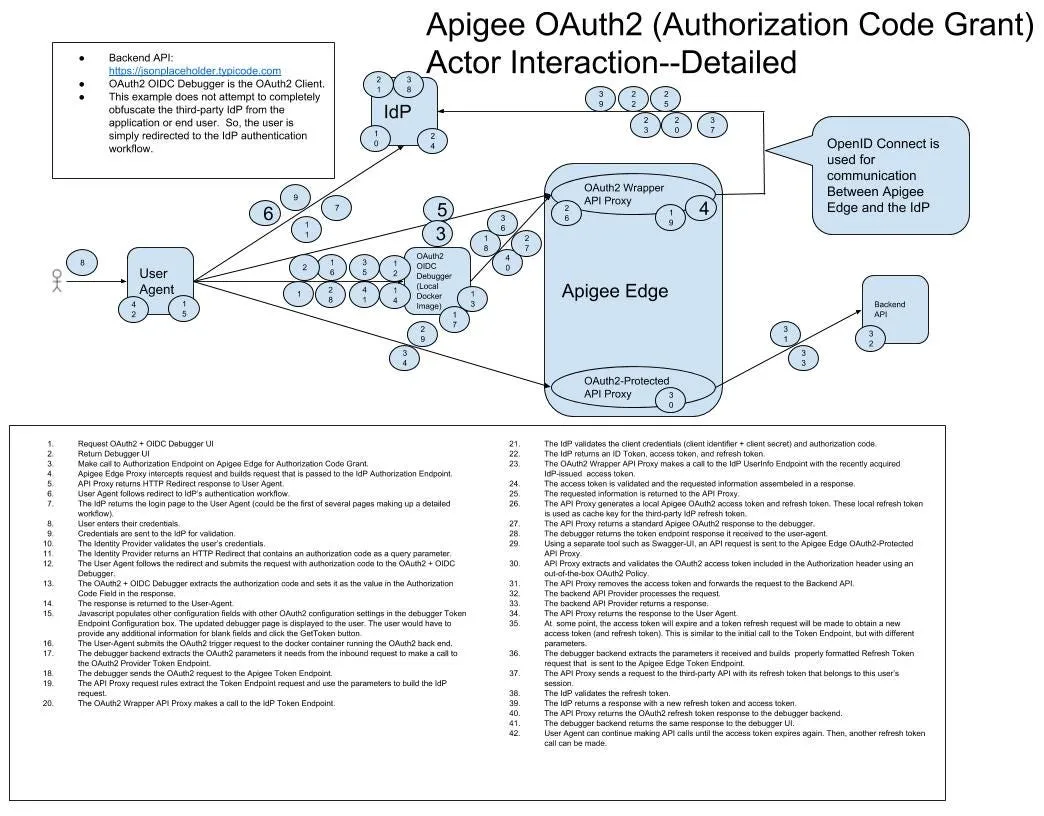
Read article: Active Directory Federation Services (ADFS) and KerberosThis post provides a detailed view of what happens when my example API Proxy that integrates Apigee Edge and a Third-Party Identity Provider for OAuth2 use cases. The setup instructions are available here.
Read article: Apigee Edge and Third-Party Identity Provider Integration — Detailed ViewI’ve been building up to more complex federation use cases over the past year. In previous posts, we explored the details of OpenID Connect(OIDC) and WS-Federation (WS-Fed). In those posts, we covered basic scenarios of how to use each protocol to integrate one Relying Party (Service Provider,…
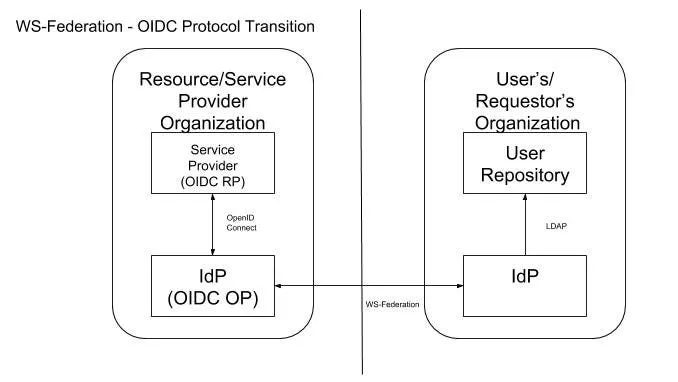
Read article: Identity Broker: An SSO Protocol Transition From OpenID Connect To WS-FederationThis blog post summarizes the details of how to deploy and configure the the Apigee Edge OAuth2 example that I put together. This example will use the OAuth2 Authorization Code Grant and Refresh Token Grant to demonstrate how OAuth2 can be used with Apigee Edge in a real-world application.
Read article: Apigee Edge OAuth2 and Third-Party Identity ProvidersThis post describes the Refresh Token support that was added to the OAuth2 + OIDC Debugger in late 2017. The OAuth2 + OIDC Debugger is a general-purpose testing tool for the OAuth2 and OpenID Connect protocols. It has been tested with many of the leading Identity Providers in the industry.
Read article: Refresh Token Support in OAuth2 + OIDC DebuggerThere are several identity protocols that are commonly supported by Identity Providers today — OAuth2, OAuth2 Token Exchange, OIDC, SAML2 Browser Profile, WS-Trust, WS-Federation, etc. The OAuth2 and OIDC protocols are relative newcomers. The other protocols have been around longer — and, tend to…
Read article: Understanding WS-Federation — Passive Requestor Profile